

The earlier you purchase our CKS exam prep the faster you pass exam CKS. Could you believe that? I can tell you that all candidates pass exam with our exam prep. Don't waste your time on one more time CKS exam. Most of our customers pass exam at first shot. What are you hesitating for? Time is money. Opportunity knocks but once. We are engaged on CKS exam prep study many years and we can guarantee you pass exam for sure. Trust me, professionals be professionals. You need to do more things what you enjoy.
Our education experts are studying Linux Foundation CKS exam prep many years. We edit all questions and answers based on real exam forecast and past real exam characters. In most situations our exam prep can include more than 80% questions of the real test. Also we make out the software version of CKS exam prep so that you can simulate the real CKS exam scene and practice more times. Our on-line APP version is popular by many young people. Studying can be more interesting and convenient anywhere. We helped more than 100000+ candidates pass exam in past. If you spend all your attention on our exam prep one or two days before the real test and master all questions and answers I believe you will pass CKS exam as what we say.

Instant Download: Upon successful payment, Our systems will automatically send the product you have purchased to your mailbox by email. (If not received within 12 hours, please contact us. Note: don't forget to check your spam.)
Not only our CKS exam prep is accurate and valid to help you pass exam but also we have good customer service. We aim to satisfy every customer at our best.
1. We guarantee all candidates can pass exam. If you fail the exam please provide us your failure mark Linux Foundation certification we will refund you all the exam prep CKS cost. No Help, Full Refund! Or you can choose to change other exam subject. (Certified Kubernetes Security Specialist (CKS))
2. Our working time is 7*24 (including the official holidays). Whenever you contact with us we will reply you in three hours. It is our pleasure to serve for you. We are happy to solve with you no matter you have any question or doubt about CKS exam prep materials or other relating information.
3. For each customer we provide one-year service warranty. We will send you the latest CKS exam prep within this year once it updates. You can ask us all questions about Linux Foundation certification examinations we try our best to reply you.
4. Our Linux Foundation department experts will check the exam prep update version. Once it updates we will refresh the website with the latest CKS version and we will send the latest version to all our customers ASAP. We make sure all CKS exam prep for sale are accurate and valid latest versions.
5. We provide the free demo download of CKS exam prep for your reference before purchasing. After you pay we will send you the download link and password for your downloading in a minute. If you find you purchase the wrong exam code we will exchange for you one time.
6. We have discount for old customers. If you stand for your company which wants to build long-term relationship with us we can talk about the discount details. Our official holiday coupon will be sent to old customers first.
If you want to know more you can contact with us in any time. Trust me, we are the best provider of CKS exam prep with high passing rate to help you pass Kubernetes Security Specialist CKS exam 100% not only our exam prep is accurate & valid but also our customer service is satisfying.
Linux Foundation CKS Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
Reference: https://training.linuxfoundation.org/certification/certified-kubernetes-security-specialist/#exams
Linux Foundation Certified Kubernetes Security Specialist (CKS) Sample Questions:
SIMULATION
use the Trivy to scan the following images,
1. amazonlinux:1
2. k8s.gcr.io/kube-controller-manager:v1.18.6
Look for images with HIGH or CRITICAL severity vulnerabilities and store the output of the same in /opt/trivy-vulnerable.txt
Correct Answer:
Send us you rsuggestion on it
SIMULATION
Documentation
Installing the Sidecar, PeerAuthentication, Deployments
You must connect to the correct host . Failure to do so may result in a zero score.
[candidate@base] $ ssh cks000041
Context
A microservices-based application using unencrypted Layer 4 (L4) transport must be secured with Istio.
Task
Perform the following tasks to secure an existing application's Layer 4 (L4) transport communication using Istio.
Istio is installed to secure Layer 4 (L4) communications.
You may use your browser to access Istio's documentation.
First, ensure that all Pods in the mtls namespace have the istio-proxy sidecar injected.
Next, configure mutual authentication in strict mode for all workloads in the mtls namespace.
Correct Answer:
See the Explanation below for complete solution
Explanation:
Below is the CKS exam-ready, step-by-step solution for QUESTION 15.
Follow exactly in this order. No extra changes.
QUESTION 15 - Istio mTLS (EXAM MODE)
1) Connect to the correct host
ssh cks000041
sudo -i
export KUBECONFIG=/etc/kubernetes/admin.conf
2) Ensure sidecar injection is enabled for the mtls namespace
2.1 Check current namespace labels
kubectl get ns mtls --show-labels
2.2 Enable automatic Istio sidecar injection
kubectl label namespace mtls istio-injection=enabled --overwrite
Verify:
kubectl get ns mtls --show-labels | grep istio-injection
Expected:
istio-injection=enabled
3) Ensure ALL Pods get the istio-proxy sidecar
Existing Pods will not get sidecars automatically.
You must restart workloads in the namespace.
3.1 Restart all Deployments in mtls
kubectl -n mtls rollout restart deployment
3.2 Verify Pods now have 2 containers (app + istio-proxy)
kubectl -n mtls get pods
Then check one Pod:
kubectl -n mtls get pod <pod-name> -o jsonpath='{.spec.containers[*].name}{"\n"}' Expected output includes:
istio-proxy
4) Configure mutual TLS (mTLS) in STRICT mode
4.1 Create a PeerAuthentication for the mtls namespace
cat <<EOF | kubectl apply -f -
apiVersion: security.istio.io/v1beta1
kind: PeerAuthentication
metadata:
name: mtls-strict
namespace: mtls
spec:
mtls:
mode: STRICT
EOF
5) Verify mTLS policy is applied
kubectl -n mtls get peerauthentication
kubectl -n mtls describe peerauthentication mtls-strict
Expected:
Mode: STRICT
6) Final verification (exam confidence check)
6.1 Confirm all Pods are Running
kubectl -n mtls get pods
6.2 Confirm sidecar injection everywhere
kubectl -n mtls get pods -o jsonpath='{range .items[*]}{.metadata.name}{" -> "}{.spec.containers[*].name}{"\n"}{end}' Each line must include istio-proxy.
SIMULATION
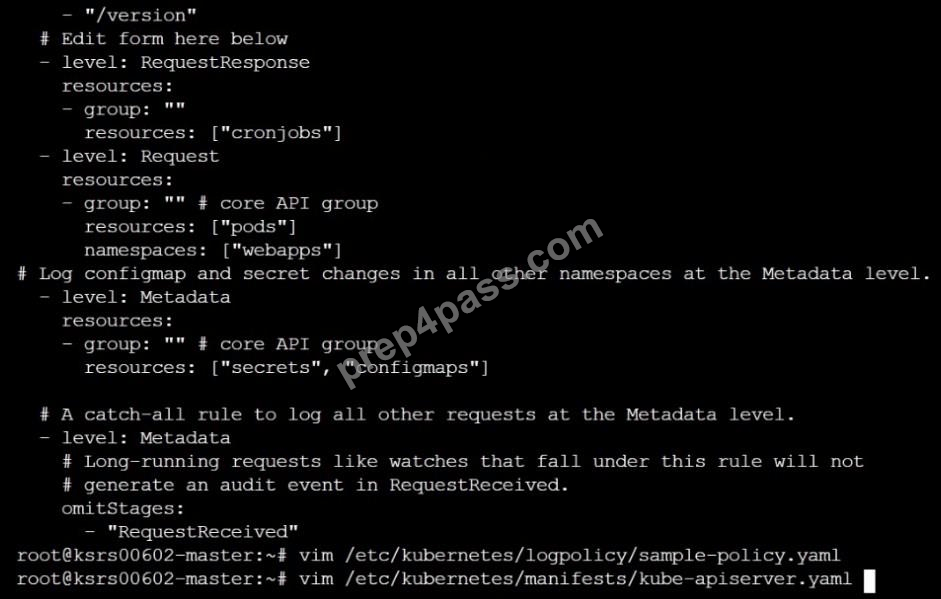
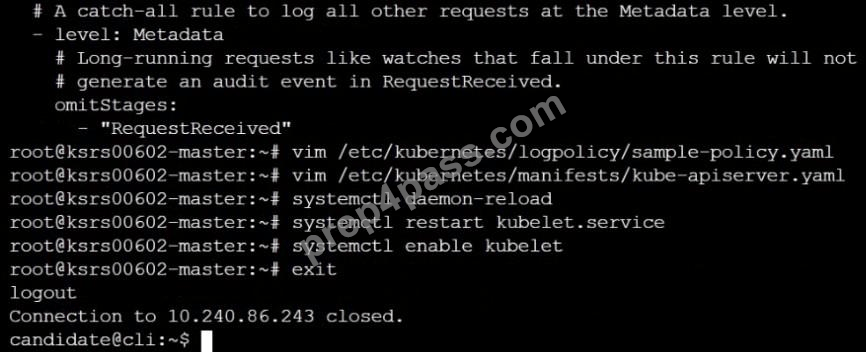
Enable audit logs in the cluster, To Do so, enable the log backend, and ensure that
1. logs are stored at /var/log/kubernetes/kubernetes-logs.txt.
2. Log files are retained for 5 days.
3. at maximum, a number of 10 old audit logs files are retained.
Edit and extend the basic policy to log:
1. Cronjobs changes at RequestResponse
2. Log the request body of deployments changes in the namespace kube-system.
3. Log all other resources in core and extensions at the Request level.
4. Don't log watch requests by the "system:kube-proxy" on endpoints or
Correct Answer:
See the Explanation belowExplanation:


SIMULATION
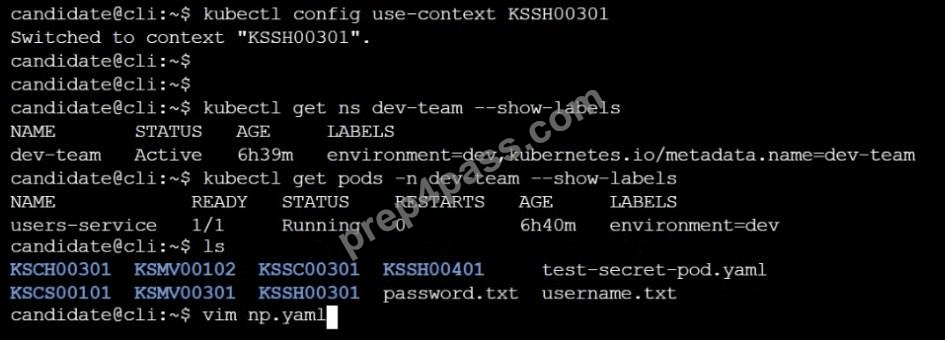
Task
Create a NetworkPolicy named pod-access to restrict access to Pod users-service running in namespace dev-team.
Only allow the following Pods to connect to Pod users-service:

Correct Answer:


SIMULATION
Context:
Cluster: gvisor
Master node: master1
Worker node: worker1
You can switch the cluster/configuration context using the following command:
[desk@cli] $ kubectl config use-context gvisor
Context: This cluster has been prepared to support runtime handler, runsc as well as traditional one.
Task:
Create a RuntimeClass named not-trusted using the prepared runtime handler names runsc.
Update all Pods in the namespace server to run on newruntime.
Correct Answer:
See the Explanation below
Explanation:
Explanation:
[desk@cli] $vim runtime.yaml
apiVersion: node.k8s.io/v1
kind: RuntimeClass
metadata:
name: not-trusted
handler: runsc
[desk@cli] $ k apply -f runtime.yaml
[desk@cli] $ k get pods
NAME READY STATUS RESTARTS AGE
nginx-6798fc88e8-chp6r 1/1 Running 0 11m
nginx-6798fc88e8-fs53n 1/1 Running 0 11m
nginx-6798fc88e8-ndved 1/1 Running 0 11m
[desk@cli] $ k get deploy
NAME READY UP-TO-DATE AVAILABLE AGE
nginx 3/3 11 3 5m
[desk@cli] $ k edit deploy nginx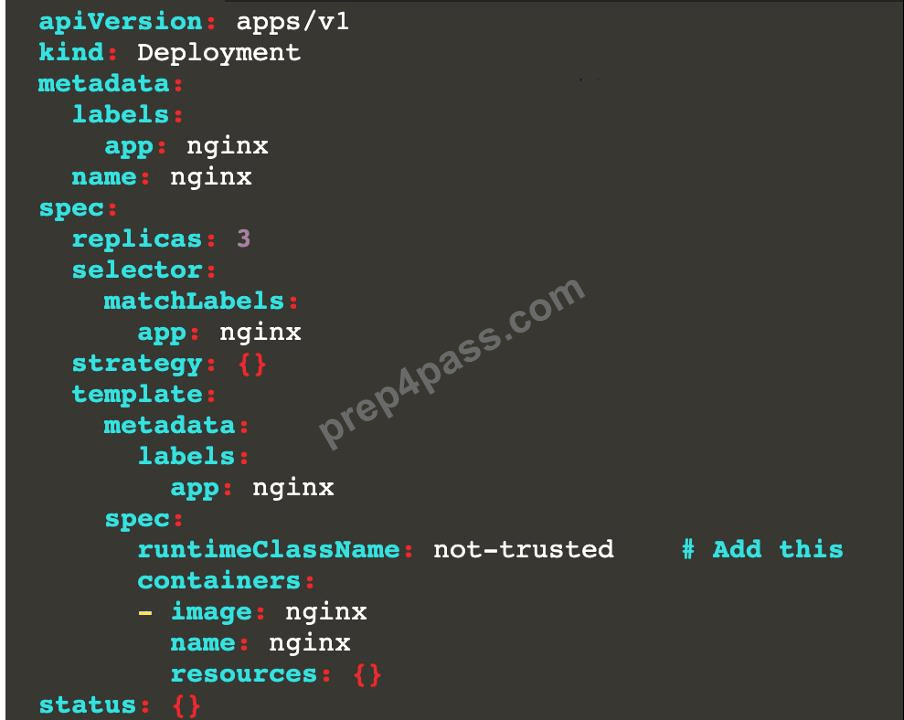
Viewing page 1 out of 14 pages.
Viewing questions 1-5 out of 66 questions.


 Enid

 Hayden
 Broderick
 Ivy
 Matthew

 Prudence
 Leopold
 Shirley
 Quintion

 Sara
 Hobart
 Griffith
 Adam
 Henry
 Larry


