

2026 Updated Verified AZ-500 dumps Q&As - Pass Guarantee or Full Refund
AZ-500 PDF Questions and Testing Engine With 517 Questions
NEW QUESTION # 76
SIMULATION
You need to enable Advanced Data Security for the SQLdb1 Azure SQL database. The solution must ensure that Azure Advanced Threat Protection (ATP) alerts are sent to [email protected].
To complete this task, sign in to the Azure portal and modify the Azure resources.
- A. * In the Azure portal, type SQL in the search box, select SQL databases from the search results then select SQLdb1. Alternatively, browse to SQL databases in the left navigation pane.
* In the properties of SQLdb1, scroll down to the Security section and select Advanced data security.
* Click on the Settings icon.
* Tick the Enable Advanced Data Security at the database level checkbox.
* In the Storage account select a storage account if one isn't selected by default.
* Under Advanced Threat Protection Settings, enter [email protected] in the Send alerts to box.
* Click the Save button to save the changes. - B. * In the Azure portal, type SQL in the search box, select SQL databases from the search results then select SQLdb1. Alternatively, browse to SQL databases in the left navigation pane.
* In the properties of SQLdb1, scroll down to the Security section and select Advanced data security.
* Click on the Settings icon.
* Tick the Enable Advanced Data Security at the database level checkbox.
* Click Yes at the confirmation prompt.
* In the Storage account select a storage account if one isn't selected by default.
* Under Advanced Threat Protection Settings, enter [email protected] in the Send alerts to box.
* Click the Save button to save the changes.
Answer: B
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/azure-sql/database/advanced-data-security
NEW QUESTION # 77
You have an Azure subscription and the computers shown in the following table.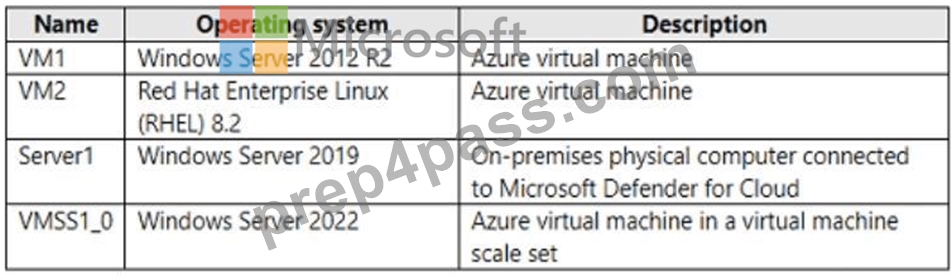
You need to perform a vulnerability scan of the computers by using Microsoft Defender for Cloud. Which computers can you scan?
- A. VM1 and VM2 only
- B. VM1, VM2, and Server1 only
- C. VM1 only
- D. VM1, VM2, Server1, and VMSS1.0
- E. Server1 and VMSS1.0 only
Answer: B
NEW QUESTION # 78
You have an Azure Active Directory (Azure AD) tenant that contains the users shown in the following table.
From Azure AD Privileged Identity Management (PIM), you configure the settings for the Security Administrator role as shown in the following exhibit.
From PIM, you assign the Security Administrator role to the following groups:
* Group1: Active assignment type, permanently assigned
* Group2: Eligible assignment type, permanently eligible
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.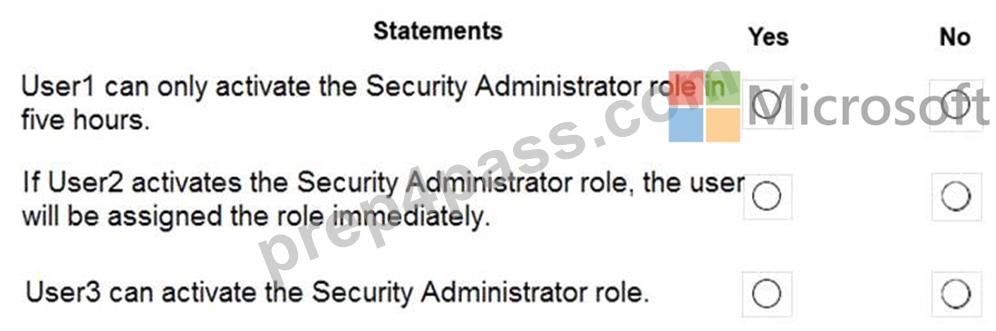
Answer:
Explanation: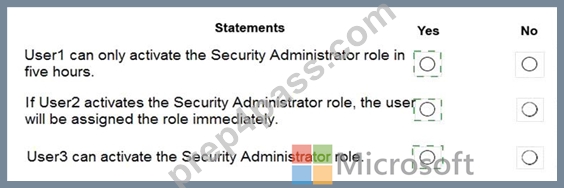
Explanation
Box 1: Yes
Eligible Type: A role assignment that requires a user to perform one or more actions to use the role. If a user has been made eligible for a role, that means they can activate the role when they need to perform privileged tasks. There's no difference in the access given to someone with a permanent versus an eligible role assignment. The only difference is that some people don't need that access all the time.
You can choose from two assignment duration options for each assignment type (eligible and active) when you configure settings for a role. These options become the default maximum duration when a user is assigned to the role in Privileged Identity Management.
Use the Activation maximum duration slider to set the maximum time, in hours, that a role stays active before it expires. This value can be from one to 24 hours.
Box 2: Yes
Active Type: A role assignment that doesn't require a user to perform any action to use the role. Users assigned as active have the privileges assigned to the role Box 3: Yes User3 is member of Group2.
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/privileged-identity-management/pim-configure
https://docs.microsoft.com/bs-cyrl-ba/azure/active-directory/privileged-identity-management/pim-resource-roles
NEW QUESTION # 79
You create an Azure subscription with Azure AD Premium P2.
You need to ensure that you can use Azure Active Directory (Azure AD) Privileged Identity Management (PIM) to secure Azure roles.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.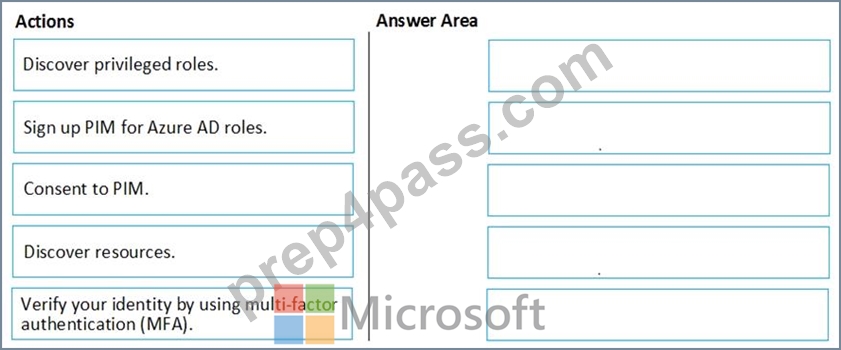
Answer:
Explanation: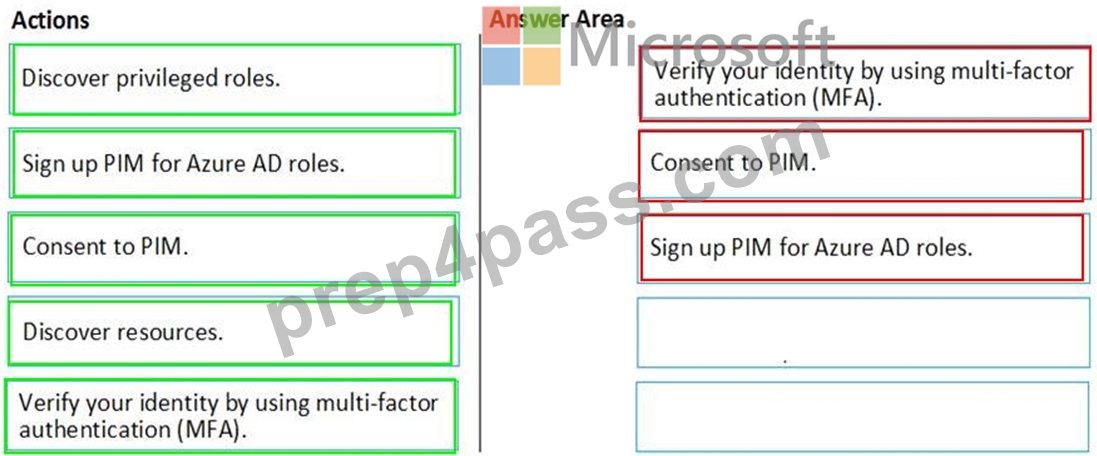
NEW QUESTION # 80
You implement the planned changes for ASG1 and ASG2.
In which NSGs can you use ASG1. and the network interfaces of which virtual machines can you assign to ASG2?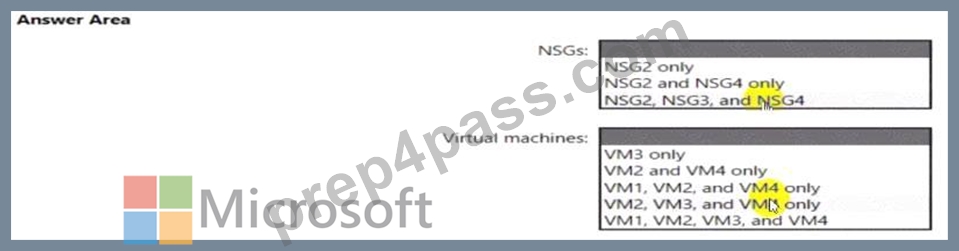
Answer:
Explanation: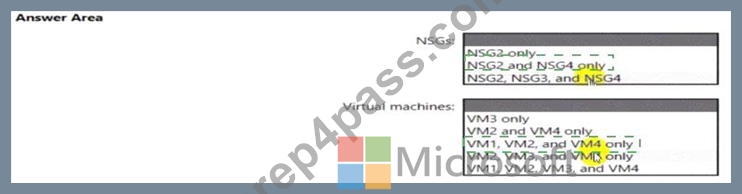
Explanation:
Graphical user interface, text, application, chat or text message Description automatically generated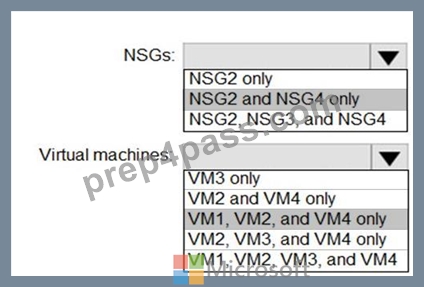
NEW QUESTION # 81
Your company has an Azure subscription named Subscription1 that contains the users shown in the following table.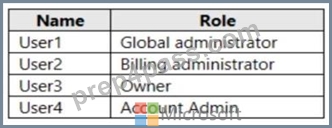
The company is sold to a new owner.
The company needs to transfer ownership of Subscription1.
Which user can transfer the ownership and which tool should the user use? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.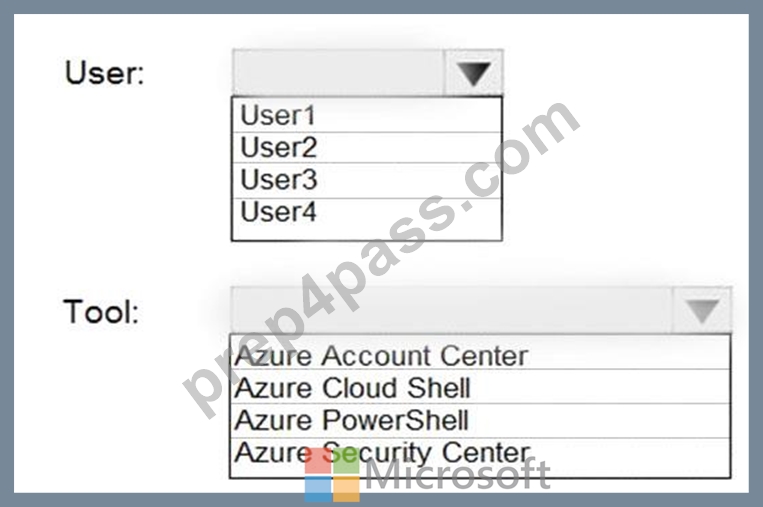
Answer:
Explanation: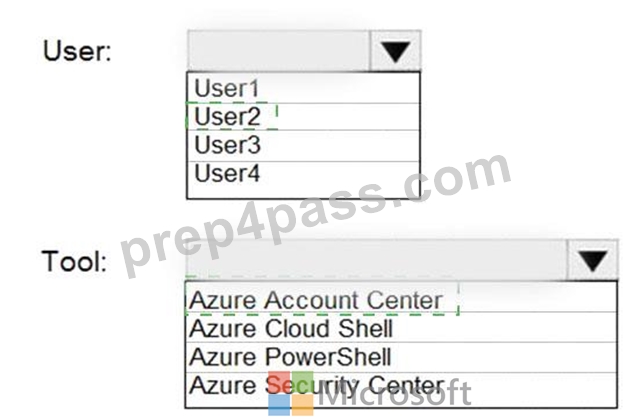
Explanation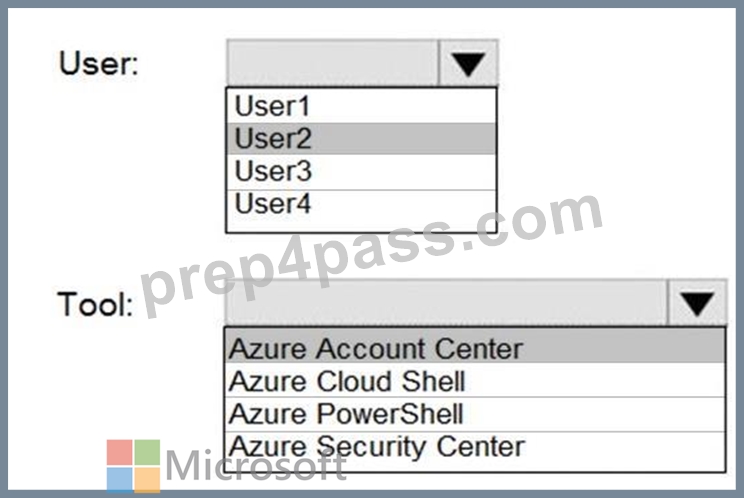
Box 1; User2
Billing Administrator
Select Transfer billing ownership for the subscription that you want to transfer.
Enter the email address of a user who's a billing administrator of the account that will be the new owner for the subscription.
Box 2: Azure Account Center
Azure Account Center can be used.
Reference:
https://docs.microsoft.com/en-us/azure/billing/billing-subscription-transfer#transfer-billing-ownership-of-an-azu
NEW QUESTION # 82
You have the Azure virtual networks shown in the following table.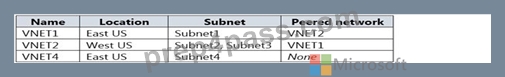
You have the Azure virtual machines shown in the following table.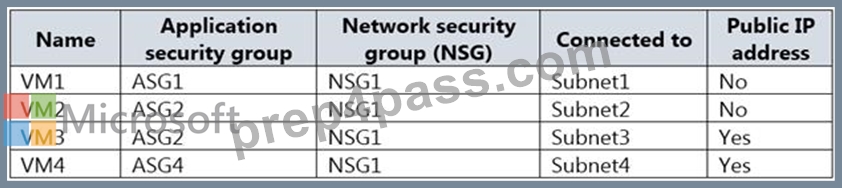
The firewalls on all the virtual machines allow ping traffic.
NSG1 is configured as shown in the following exhibit.
Inbound security rules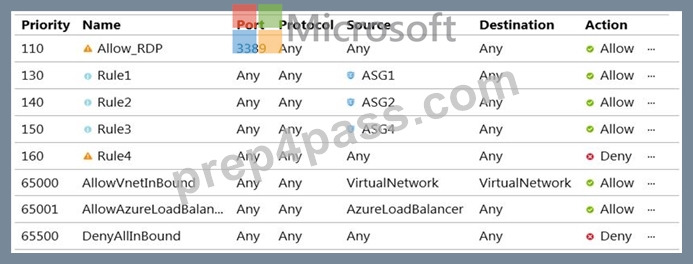
Outbound security rules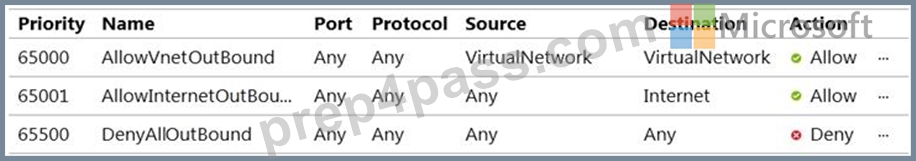
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.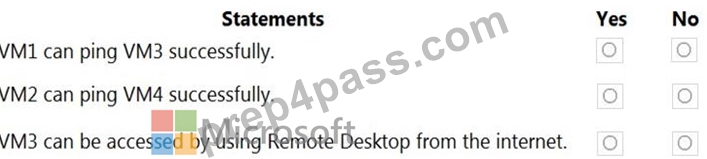
Answer:
Explanation: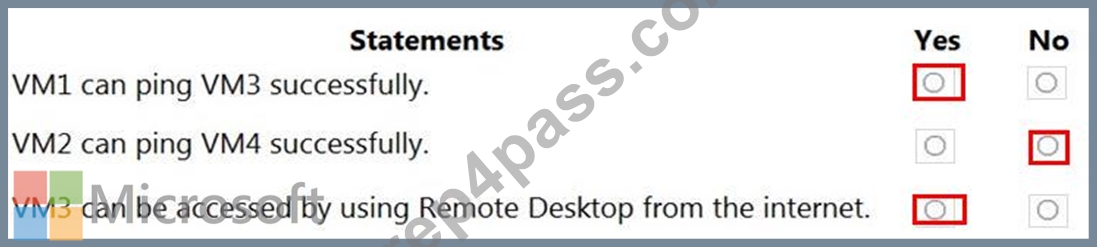
NEW QUESTION # 83
You have an Azure subscription that is linked to an Azure AD tenant and contains the virtual machines shown in the following table.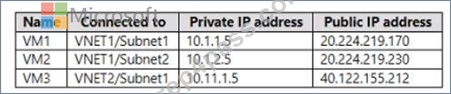
The subnets of the virtual networks have the service endpoints shown in the following table.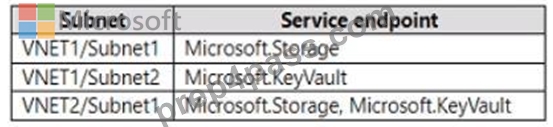
You create the resources shown in the following table.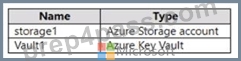
For each of the following statements, select Yes if the statement is true. Otherwise, select No. NOTE: Each correct selection is worth one point.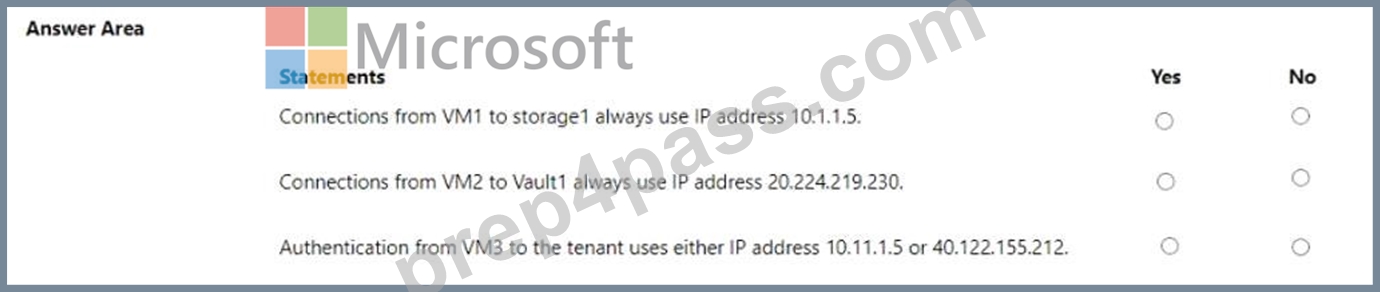
Answer:
Explanation: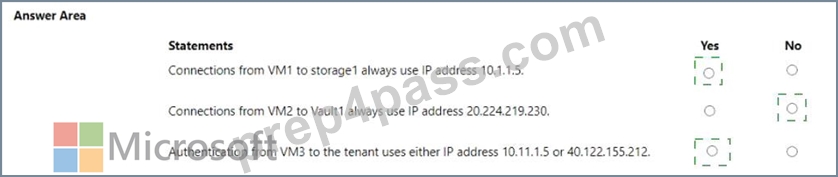
Explanation: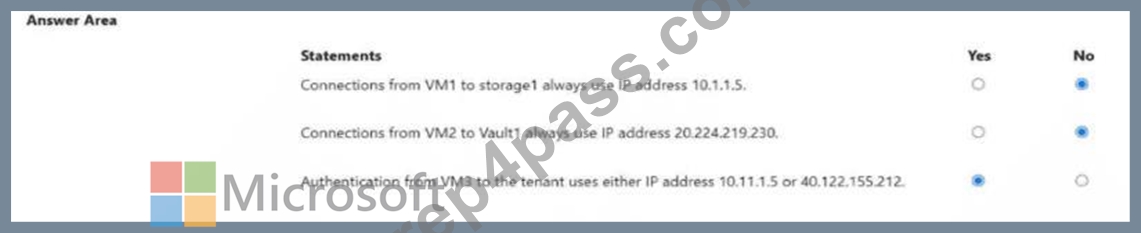
NEW QUESTION # 84
You need to create Role1 to meet the platform protection requirements.
How should you complete the role definition of Role1? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.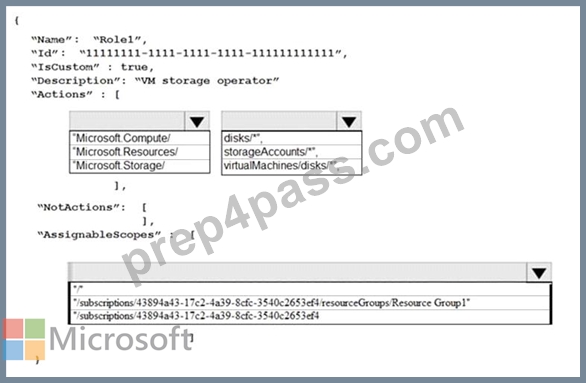
Answer:
Explanation: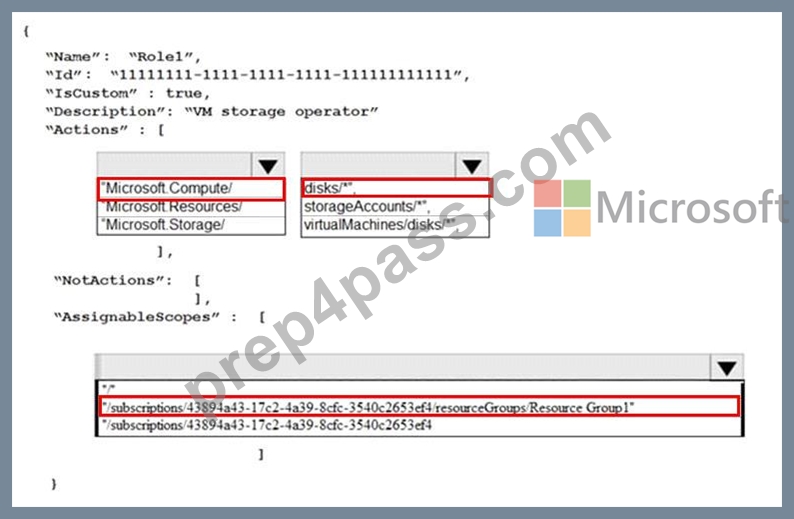
NEW QUESTION # 85
You have an Azure subscription that is linked to an Azure AD tenant and contains the resources shown in the following table.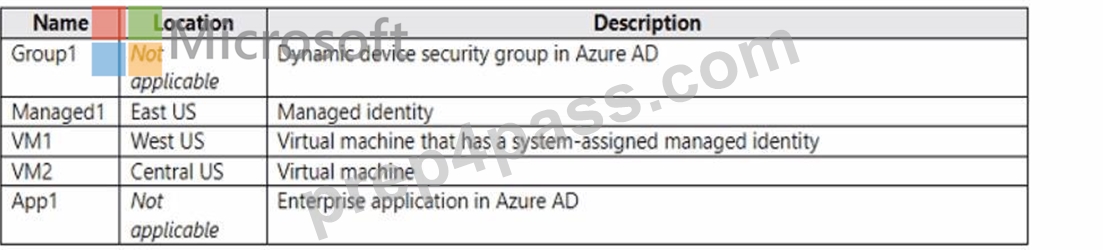
Which resources can be assigned the Contributor role for VM1?
- A. Managed1 and App1 only
- B. Group1, Managed1, VM1. and App1 only
- C. Group1. Managed1, and VM2only
- D. Group1 and Managed1 only
Answer: A
NEW QUESTION # 86
You are evaluating the effect of the application security groups on the network communication between the virtual machines in Sub2.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.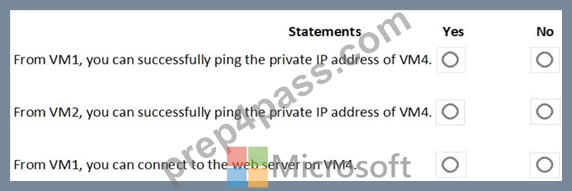
Answer:
Explanation:
Explanation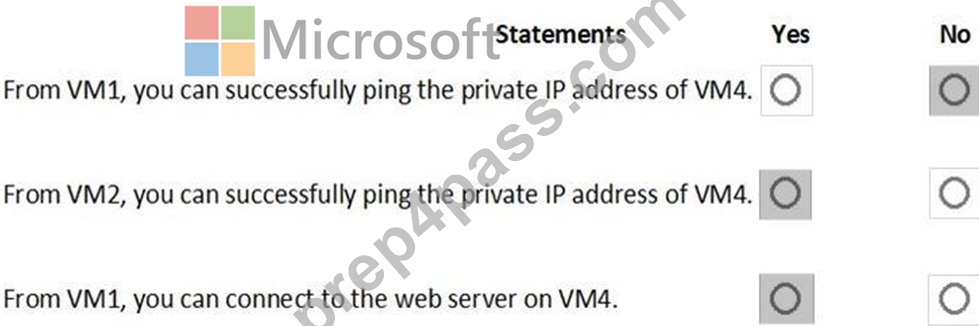
Box 1: No. VM4 is in Subnet13 which has NSG3 attached to it.
VM1 is in ASG1. NSG3 would only allow ICMP pings from ASG2 but not ASG1. Only TCP traffic is allowed from ASG1.
NSG3 has the inbound security rules shown in the following table.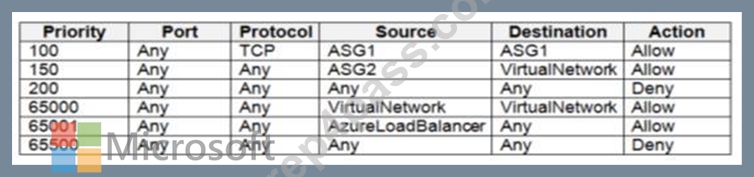
Box 2: Yes.
VM2 is in ASG2. Any protocol is allowed from ASG2 so ICMP ping would be allowed.
Box3. VM1 is in ASG1. TCP traffic is allowed from ASG1 so VM1 could connect to the web server as connections to the web server would be on ports TCP 80 or TCP 443.
NEW QUESTION # 87
You have an Azure App Service web app named App1 as shown in the following exhibit.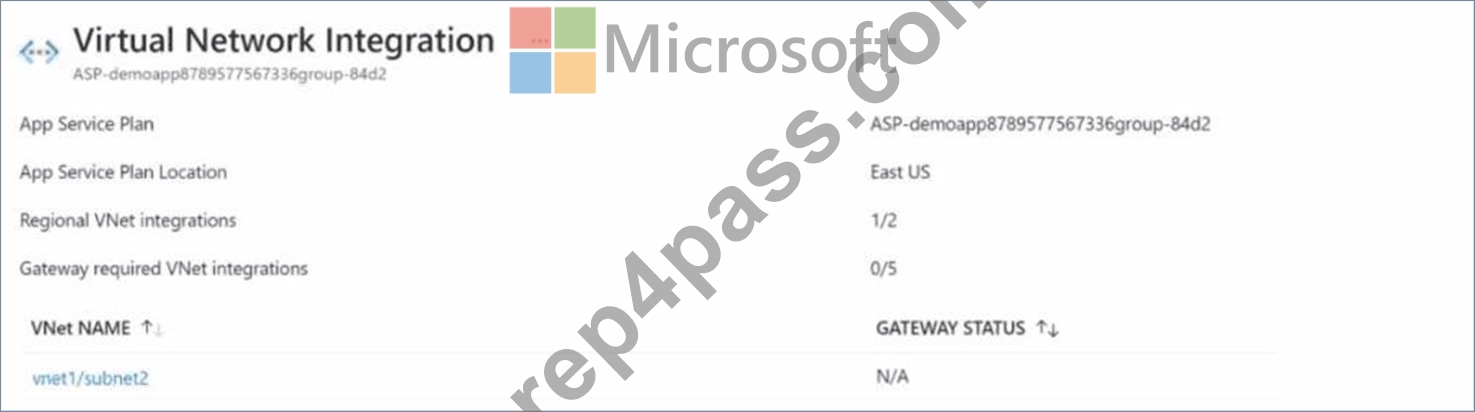
Subnet 2 contains a virtual machine named VM1.
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic NOTE: Each correct selection is worth one point.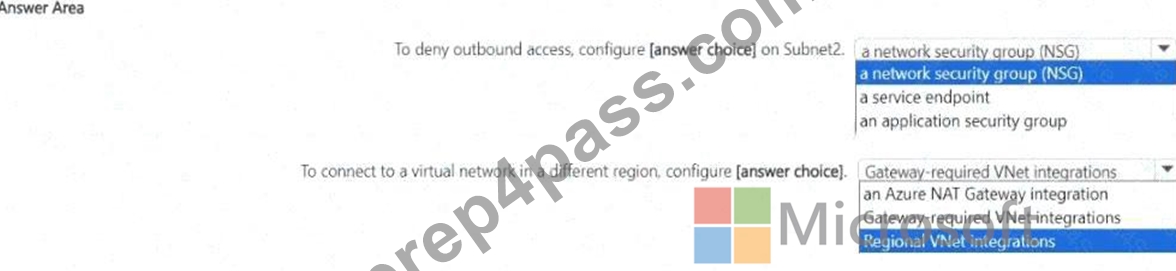
Answer:
Explanation: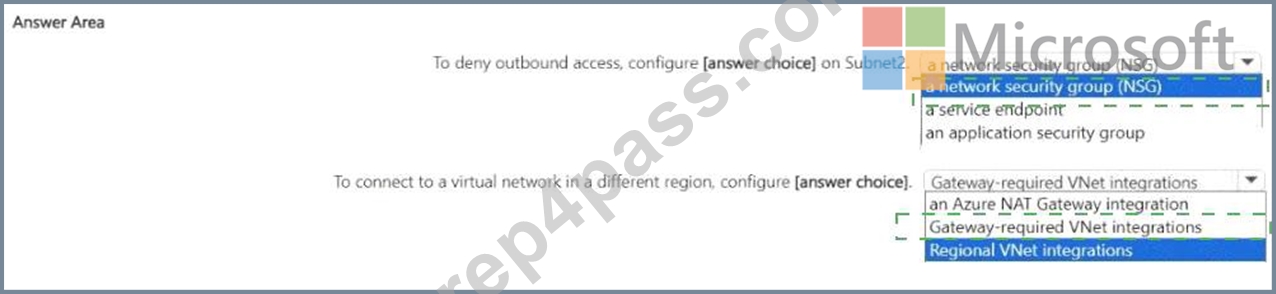
Explanation: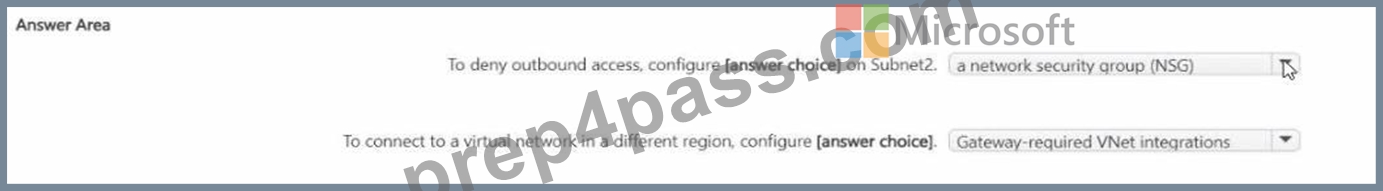
NEW QUESTION # 88
You have an Azure Container Registry named ContReg1 that contains a container image named image1.
You enable content trust for ContReg1.
After content trust is enabled, you push two images to ContReg1 as shown in the following table.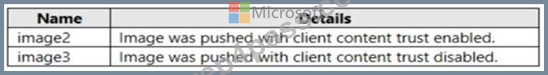
Which images are trusted images?
- A. image1 and image2 only
- B. image2 only
- C. image1, image2, and image3
Answer: B
Explanation:
Azure Container Registry implements Docker's content trust model, enabling pushing and pulling of signed images.
To push a trusted image tag to your container registry, enable content trust and push the image with docker push.
To work with trusted images, both image publishers and consumers need to enable content trust for their Docker clients. As a publisher, you can sign the images you push to a content trust-enabled registry.
Reference:
https://docs.microsoft.com/en-us/azure/container-registry/container-registry-content-trust Manage security operations Testlet 1 Case Study This is a case study. Case studies are not timed separately. You can use as much exam time as you would like to complete each case. However, there may be additional case studies and sections on this exam. You must manage your time to ensure that you are able to complete all questions included on this exam in the time provided.
To answer the questions included in a case study, you will need to reference information that is provided in the case study. Case studies might contain exhibits and other resources that provide more information about the scenario that is described in the case study. Each question is independent of the other question on this case study.
At the end of this case study, a review screen will appear. This screen allows you to review your answers and to make changes before you move to the next sections of the exam. After you begin a new section, you cannot return to this section.
To start the case study
To display the first question on this case study, click the Next button. Use the buttons in the left pane to explore the content of the case study before you answer the questions. Clicking these buttons displays information such as business requirements, existing environment, and problem statements. If the case study has an All Information tab, note that the information displayed is identical to the information displayed on the subsequent tabs. When you are ready to answer a question, click the Question button to return to the question.
Overview
Contoso, Ltd. is a consulting company that has a main office in Montreal and two branch offices in Seattle and New York.
The company hosts its entire server infrastructure in Azure.
Contoso has two Azure subscriptions named Sub1 and Sub2. Both subscriptions are associated to an Azure Active Directory (Azure AD) tenant named contoso.com.
Existing Environment
Azure AD
Contoso.com contains the users shown in the following table.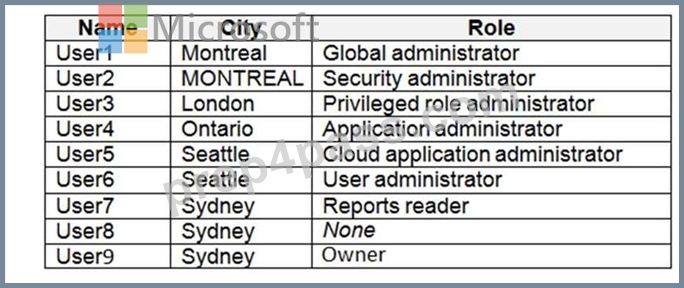
Contoso.com contains the security groups shown in the following table.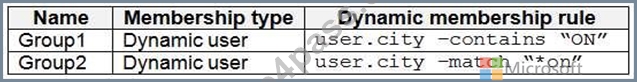
Sub1
Sub1 contains six resource groups named RG1, RG2, RG3, RG4, RG5, and RG6.
User9 creates the virtual networks shown in the following table.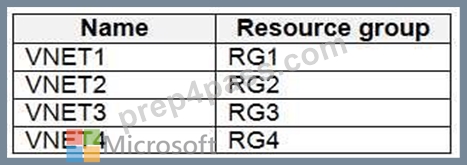
Sub1 contains the locks shown in the following table.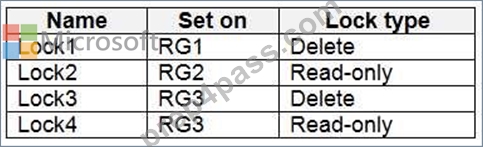
Sub1 contains the Azure policies shown in the following table.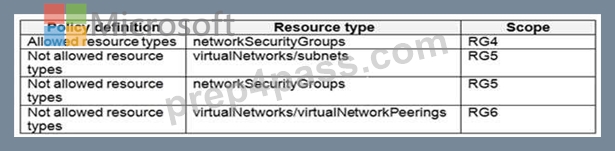
Sub2
Sub2 contains the virtual networks shown in the following table.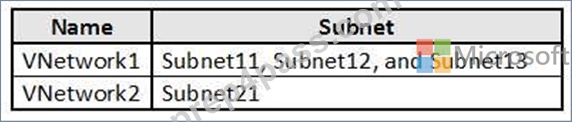
Sub2 contains the virtual machines shown in the following table.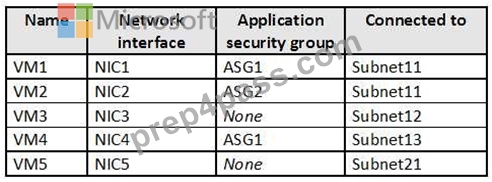
All virtual machines have public IP addresses and the Web Server (IIS) role installed. The firewalls for each virtual machine allow ping requests and web requests.
Sub2 contains the network security groups (NSGs) shown in the following table.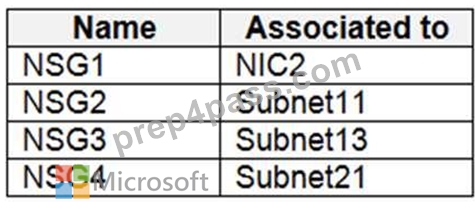
NSG1 has the inbound security rules shown in the following table.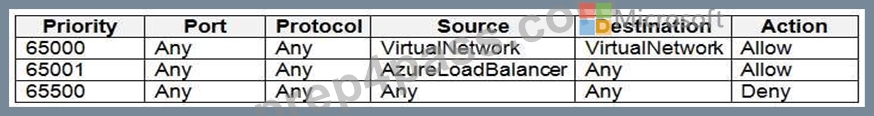
NSG2 has the inbound security rules shown in the following table.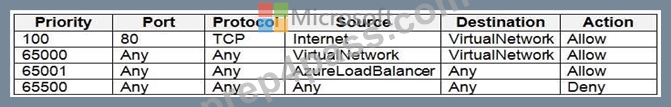
NSG3 has the inbound security rules shown in the following table.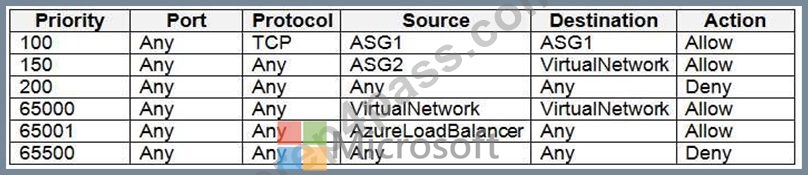
NSG4 has the inbound security rules shown in the following table.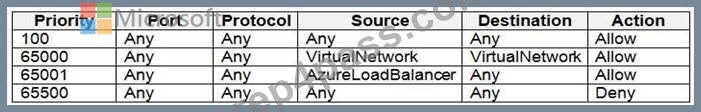
NSG1, NSG2, NSG3, and NSG4 have the outbound security rules shown in the following table.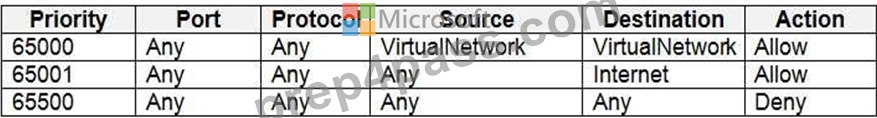
Technical requirements
Contoso identifies the following technical requirements:
* Deploy Azure Firewall to VNetwork1 in Sub2.
* Register an application named App2 in contoso.com.
* Whenever possible, use the principle of least privilege.
* Enable Azure AD Privileged Identity Management (PIM) for contoso.com.
Manage security operations
Testlet 2
This is a case study. Case studies are not timed separately. You can use as much exam time as you would like to complete each case. However, there may be additional case studies and sections on this exam. You must manage your time to ensure that you are able to complete all questions included on this exam in the time provided.
To answer the questions included in a case study, you will need to reference information that is provided in the case study. Case studies might contain exhibits and other resources that provide more information about the scenario that is described in the case study. Each question is independent of the other question on this case study.
At the end of this case study, a review screen will appear. This screen allows you to review your answers and to make changes before you move to the next sections of the exam. After you begin a new section, you cannot return to this section.
To start the case study
To display the first question on this case study, click the Next button. Use the buttons in the left pane to explore the content of the case study before you answer the questions. Clicking these buttons displays information such as business requirements, existing environment, and problem statements. If the case study has an All Information tab, note that the information displayed is identical to the information displayed on the subsequent tabs. When you are ready to answer a question, click the Question button to return to the question.
Overview
Litware, Inc. is a digital media company that has 500 employees in the Chicago area and 20 employees in the San Francisco area.
Existing Environment
Litware has an Azure subscription named Sub1 that has a subscription ID of 43894a43-17c2-4a39-8cfc-
3540c2653ef4.
Sub1 is associated to an Azure Active Directory (Azure AD) tenant named litwareinc.com. The tenant contains the user objects and the device objects of all the Litware employees and their devices. Each user is assigned an Azure AD Premium P2 license. Azure AD Privileged Identity Management (PIM) is activated.
The tenant contains the groups shown in the following table.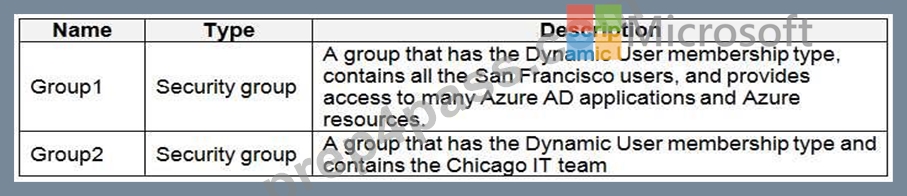
The Azure subscription contains the objects shown in the following table.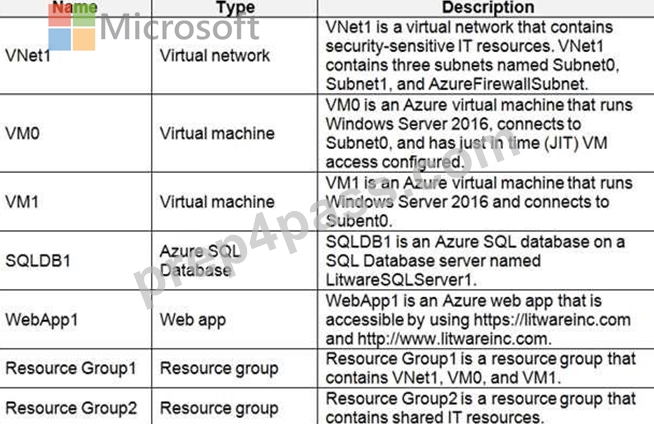
Azure Security Center is set to the Free tier.
Planned changes
Litware plans to deploy the Azure resources shown in the following table.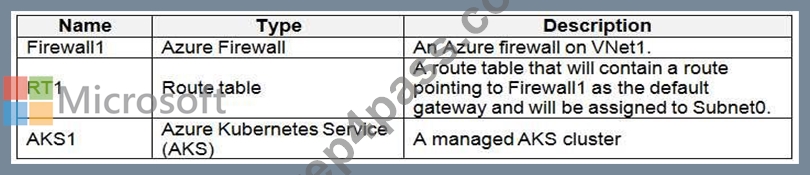
Identity and Access Requirements
Litware identifies the following identity and access requirements:
* All San Francisco users and their devices must be members of Group1.
* The members of Group2 must be assigned the Contributor role to Resource Group2 by using a permanent eligible assignment.
* Users must be prevented from registering applications in Azure AD and from consenting to applications that access company information on the users' behalf.
Platform Protection Requirements
Litware identifies the following platform protection requirements:
* Microsoft Antimalware must be installed on the virtual machines in Resource Group1.
* The members of Group2 must be assigned the Azure Kubernetes Service Cluster Admin Role.
* Azure AD users must be to authenticate to AKS1 by using their Azure AD credentials.
* Following the implementation of the planned changes, the IT team must be able to connect to VM0 by using JIT VM access.
* A new custom RBAC role named Role1 must be used to delegate the administration of the managed disks in Resource Group1. Role1 must be available only for Resource Group1.
Security Operations Requirements
Litware must be able to customize the operating system security configurations in Azure Security Center.
Data and Application Requirements
Litware identifies the following data and applications requirements:
* The users in Group2 must be able to authenticate to SQLDB1 by using their Azure AD credentials.
* WebApp1 must enforce mutual authentication.
General Requirements
Litware identifies the following general requirements:
* Whenever possible, administrative effort must be minimized.
* Whenever possible, use of automation must be minimized.
NEW QUESTION # 89
You have an Azure Kubernetes Service (AKS) cluster that will connect to an Azure Container Registry.
You need to use automatically generated service principal for the AKS cluster to authenticate to the Azure Container Registry.
What should you create?
- A. a role assignment
- B. an Azure Active Directory (Azure AD) user
- C. a secret in Azure Key Vault
- D. an Azure Active Directory (Azure AD) group
Answer: A
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/aks/kubernetes-service-principal
NEW QUESTION # 90
You have the Azure virtual machines shown in the following table.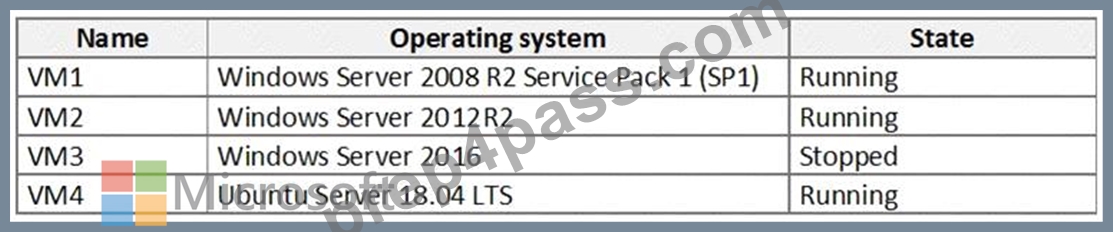
For which virtual machine can you enable Update Management?
- A. VM2 and VM3 only
- B. VM1, VM2, VM3, and VM4
- C. VM2, VM3, and VM4 only
- D. VM1, VM2, and VM4 only
- E. VM1, VM2, and VM3 only
Answer: D
Explanation:
References:
https://docs.microsoft.com/en-us/azure/automation/automation-update-management?toc=%2Fazure%2Fautomati
NEW QUESTION # 91
You have the Azure key vaults shown in the following table.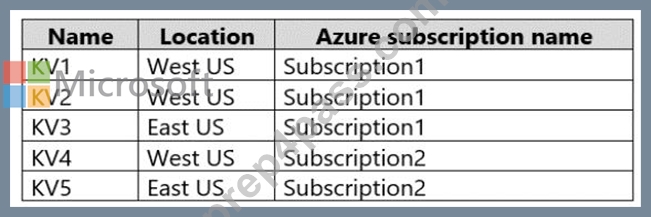
KV1 stores a secret named Secret1 and a key for a managed storage account named Key1.
You back up Secret1 and Key1.
To which key vaults can you restore each backup? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.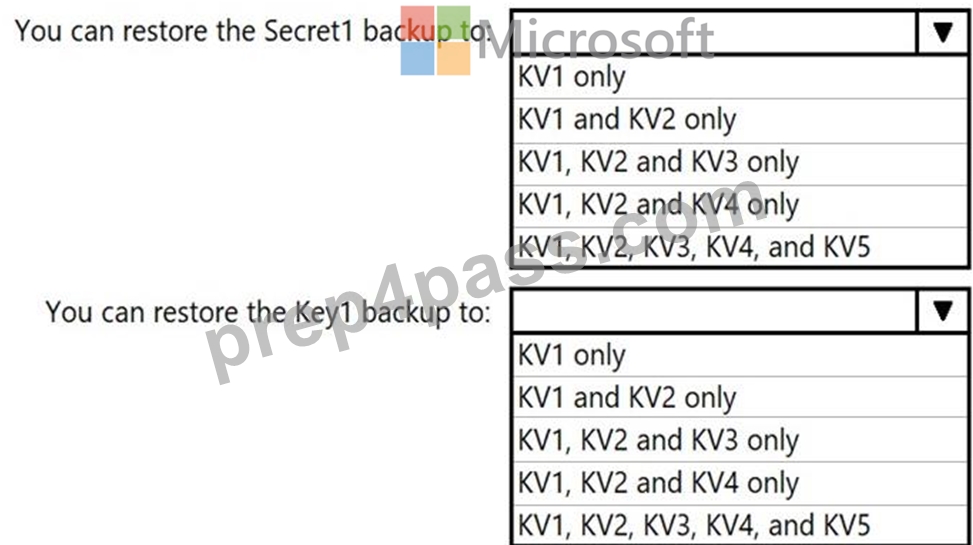
Answer:
Explanation: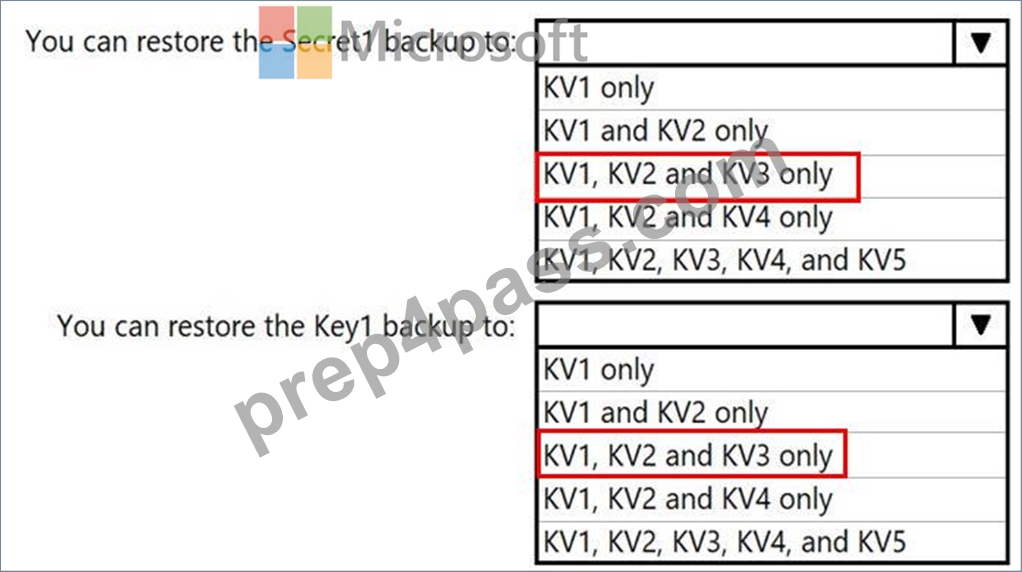
NEW QUESTION # 92
You need to ensure that users can access VM0. The solution must meet the platform protection requirements.
What should you do?
- A. Assign RT1 to AzureFirewallSubnet.
- B. On Firewall, configure a DNAT rule.
- C. On Firewall, configure a network traffic filtering rule.
- D. Move VM0 to Subnet1.
Answer: D
Explanation:
Azure Firewall has the following known issue:
Conflict with Azure Security Center (ASC) Just-in-Time (JIT) feature.
If a virtual machine is accessed using JIT, and is in a subnet with a user-defined route that points to Azure Firewall as a default gateway, ASC JIT doesn't work. This is a result of asymmetric routing - a packet comes in via the virtual machine public IP (JIT opened the access), but the return path is via the firewall, which drops the packet because there is no established session on the firewall.
Solution: To work around this issue, place the JIT virtual machines on a separate subnet that doesn't have a user-defined route to the firewall.
Scenario: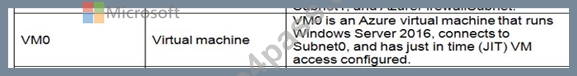
Following the implementation of the planned changes, the IT team must be able to connect to VM0 by using JIT VM access.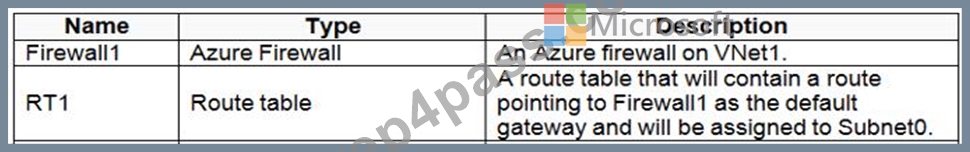
References:
https://docs.microsoft.com/en-us/azure/firewall/overview
NEW QUESTION # 93
You have an azure active Directory (Azure AD) tenant that contains the resources shown in the following table.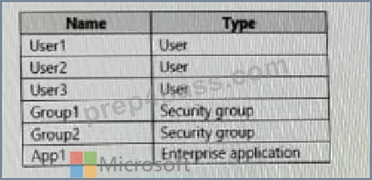
User2 is the owner of Group2.
The user and group settings for App1 are configured as shown in the following exhibit.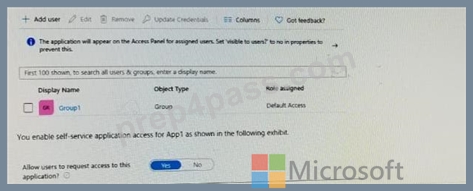
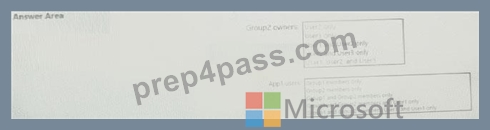
Answer:
Explanation: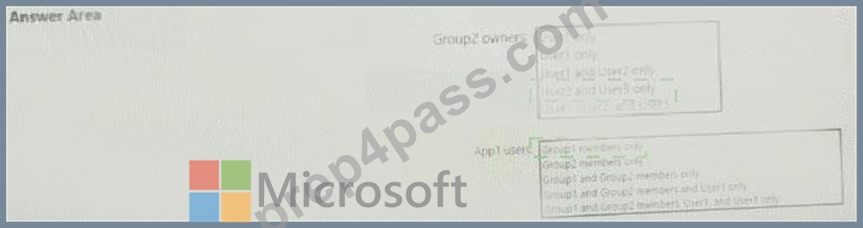
NEW QUESTION # 94
You have an Azure subscription that contains the key vaults shown in the following table.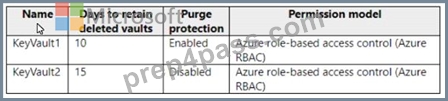
The subscription contains the users shown in the following table.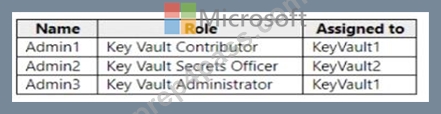
On June 1, you perform the following actions:
* Delete a key named key1 from KeyVault1.
* Delete a secret named secret 1 from KeyVault2.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.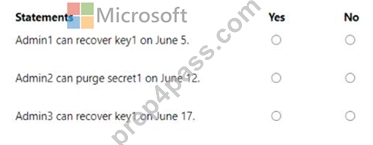
Answer:
Explanation: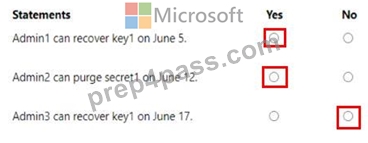
NEW QUESTION # 95
You have a management group named MG1 that contains an Azure subscription and a resource group named RG1. RG1 contains a virtual machine named VM1. You have the custom Azure roles shown in the following table.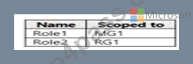
The permissions for Role1 are shown in the following role definition file.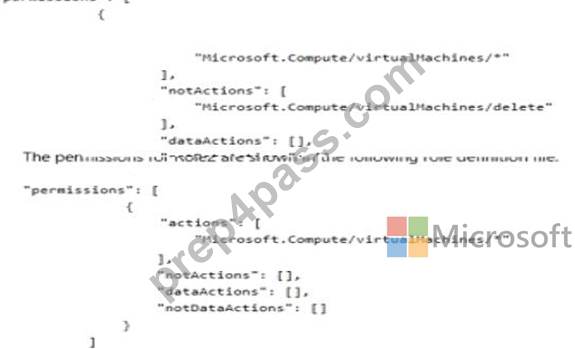
You assign the roles to the users shown in the following table.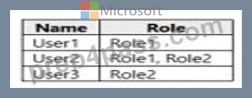
For each of the following statements, select Yes if the statement is true. Otherwise, select No NOTE: Each correct selection is worth one point.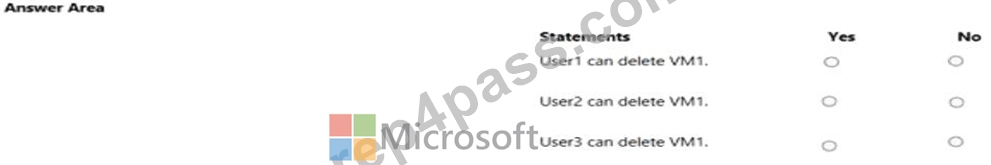
Answer:
Explanation: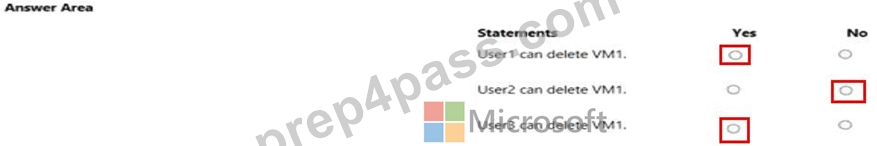
NEW QUESTION # 96
......
To sum up, the Microsoft AZ-500: Microsoft Azure Security Technologies exam is an excellent opportunity for individuals who want to validate their skills in Azure security. AZ-500 exam covers a broad range of topics related to securing data, applications, and networks in Microsoft Azure. Passing the exam gives the candidate a Microsoft Certified: Azure Security Engineer Associate certification, which is highly valued in the industry.
Exam Engine for AZ-500 Exam Free Demo & 365 Day Updates: https://www.prep4pass.com/AZ-500_exam-braindumps.html
Test Engine to Practice Test for AZ-500 Valid and Updated Dumps: https://drive.google.com/open?id=1qL9C7KVEtq3CzdI2t6NM0VFyM11SfB8A
