

Free CIS-DF pdf Files With Updated and Accurate Dumps Training
Top-Class CIS-DF Question Answers Study Guide
NEW QUESTION # 21
A CMDB Manager wants to improve data quality using theCMDB Health Dashboard.
What needs to happen to generate CMDB health scores?
- A. Nothing, CMDB health scores are calculated by default
- B. The plugin, CMDB health calculation, needs to be installed
- C. The scheduled jobs for the CMDB Health Dashboard must be activated
Answer: C
Explanation:
InServiceNow, theCMDB Health Dashboarddoes not calculate health scores in real time by default. Instead, health scores are generated and refreshed byscheduled calculation jobsthat evaluate CI data against defined health rules across the dimensions ofcompleteness, correctness, and compliance.
To generate and maintain CMDB health scores, thescheduled jobs for CMDB Health must be active. These jobs periodically scan the CMDB, apply health rules (for example, required attributes populated, lifecycle status compliance, certification results), and calculate scores that are displayed on the dashboard and scorecards. Without these scheduled jobs running, the dashboard cannot produce current or meaningful health metrics.
Option B is incorrect because CMDB health scoring isnot automatic or real-time; it depends on scheduled processing. Option C is also incorrect because CMDB Health is part of the core CMDB/Data Foundations capability in ServiceNow and does not require a separate "CMDB health calculation" plugin to be installed in modern implementations.
Activating and maintaining these scheduled jobs ensures that health scores remain accurate, trendable over time, and useful for governance decisions. This is a foundational requirement for using the CMDB Health Dashboard as a data quality improvement tool.
Therefore, the correct answer isA - The scheduled jobs for the CMDB Health Dashboard must be activated.
NEW QUESTION # 22
The CMDB Administrator group aims to display meaningful results on theCMDB Health Dashboard - Compliance Scorecardforserver records that are not on the latest patch.
What must be configured to achieve this goal?
- A. Certification Policies, Data Filters, Scheduled Jobs
- B. Stale, Orphan, Duplicate
- C. Technical Service Offerings, Dynamic CI Groups, CMDB Groups
- D. Certification Filter, Certification Template, Audit
Answer: A
Explanation:
InServiceNow, theCompliancedimension of the CMDB Health Dashboard is driven byData Certification. To surface meaningful compliance results-such as identifying servers that arenot on the latest patch-the platform requires a combination ofCertification Policies,Data Filters, andScheduled Jobs.
Certification Policiesdefinewhatdata must be validated andwhich attributesare subject to compliance checks (for example, patch level, OS version, or last update date).Data Filtersscope the population-such as server classes only-ensuring the compliance evaluation targets the correct CIs.Scheduled Jobsautomate when certifications run, keeping compliance scores current and reflective of the latest state.
Options A and C are incorrect becauseauditsandstale/orphan/duplicatechecks relate to other health dimensions (correctness and completeness), not compliance. Option B focuses on service modeling and group alignment, which does not directly drive compliance scoring for patch currency.
Therefore, configuringCertification Policies, Data Filters, and Scheduled Jobsis required to accurately measure and display patch compliance on the CMDB Health Dashboard.
NEW QUESTION # 23
Multiple discovery sources (ServiceNow Discovery and a third-party tool) are creating duplicate Server CIs. What should you configure to prevent duplicates moving forward?
- A. Business Rules
- B. Data Certification
- C. Identification Rules
- D. Transform Map Coalesce
Answer: C
Explanation:
The Identification Rule determines how CIs are uniquely identified. Proper identification criteria (e.g., serial number + hostname) prevents duplicate CI creation across sources via the IRE.
NEW QUESTION # 24
A Configuration Manager is planning the implementation of the CMDB.
Which is theprescribed CSDM rollout order?
- A. Crawl, Walk, Run, Fly
- B. Initiate, Plan, Execute, Deliver, Close
- C. Architecture, Business, Technical, Governance
- D. Initial, Developing, Defined, Managed
Answer: A
Explanation:
TheCommon Service Data Model (CSDM)prescribes anincremental, maturity-based rollout approachto reduce risk and ensure sustainable adoption. The recommended order isCrawl, Walk, Run, Fly, which aligns implementation effort with increasing organizational capability and value realization.
Crawlfocuses on foundational data hygiene: core CI classes, identification rules, reconciliation, basic Discovery ingestion, and CMDB Health basics.
Walkintroduces service context, includingBusiness Services, Application Services, and relationships that enable impact analysis for Incident and Change.
Runexpands into operational excellence withService Mapping, service offerings, advanced governance, and process automation.
Flyrepresents optimization and scale, leveraging analytics, AI/ML, proactive operations, and cross-domain integration (e.g., SecOps, APM, CSM).
This progression ensures teams do not over-model early or introduce complexity before data quality and governance are established. The other options describe generic project lifecycles or organizational categorizations, not the CSDM-recommended adoption path.
Therefore, the correct answer isD - Crawl, Walk, Run, Fly.
NEW QUESTION # 25
A CMDB Administrator is leveraging CI data as part of an Integrated Risk Management (IRM) implementation and the Entity Scoping process. The Administrator wants to leverage the CSDM Data Foundations Dashboard playbooks under the Run tab.
Which CSDM relationships are leveraged using the CSDM playbooks? (Choose two)
- A. Locations that have established parent records
- B. Logical CIs that have relationships with Information Objects
- C. Business Applications that have relationships to Application Services
- D. Business Applications that have their relationships to Information Objects
Answer: B,D
Explanation:
The Run tab in the CSDM Data Foundations Dashboard focuses on enabling operationalized, risk- aware use cases, including Integrated Risk Management (IRM) and Entity Scoping. These use cases require organizations to understand what data is processed, where it resides, and which technical components are involved, rather than only service impact for ITSM.
Information Objects play a central role at this stage.
Option A is correct because Business Applications related to Information Objects allow organizations to identify what types of data (PII, PCI, PHI, regulated data) are processed by each business application. This relationship is essential for risk classification, regulatory compliance, and audit scoping in IRM. Without it, risk assessments lack data sensitivity context.
Option D is also correct because Logical CIs (such as databases, schemas, or data stores) related to Information Objects establish where sensitive data is stored or processed at a technical level. This enables IRM to trace risk from business context down to technical exposure, supporting control testing, issue management, and remediation prioritization.
NEW QUESTION # 26
A CMDB Administrator needs to import external data into the CMDB. To reduce the risk of creating duplicates and prevent updates from unauthorized sources, it must be ensured that the Identification and Reconciliation Engine (IRE) is not bypassed.
What is the recommended method to import data into the CMDB utilizing the Identification and Reconciliation API?
- A. Import Sets and Transform Maps
- B. IntegrationHub ETL
- C. Table API (REST API or SOAP API)
Answer: B
Explanation:
In ServiceNow, protecting CMDB data quality during ingestion is a core Data Foundations principle. The Identification and Reconciliation Engine (IRE) is designed to ensure that CI records are uniquely identified, merged correctly, and protected from unauthorized overwrites. Any ingestion method that bypasses IRE introduces a high risk of duplicates and data corruption.
IntegrationHub ETL is the recommended method because it is natively designed to work with the Identification and Reconciliation API. When properly configured, IntegrationHub ETL ensures that incoming data is processed through IRE, applying identification rules, reconciliation rules, and source precedence. This allows multiple data sources to coexist safely while maintaining CMDB integrity.
Option B (Table API) is explicitly discouraged for CMDB ingestion because it writes directly to CMDB tables and bypasses IRE entirely, making it one of the most common causes of duplicate and conflicting CI records. While REST and SOAP APIs are powerful, they are not safe for CMDB ingestion unless they explicitly invoke the IRE API, which most generic table integrations do not.
Option C (Import Sets and Transform Maps) can be configured to call IRE, but this requires additional scripting and strict governance. Because of this complexity and higher risk of misconfiguration, it is not the recommended approach when safer, purpose-built options exist.
Therefore, IntegrationHub ETL is the verified and best-practice answer, making Option A correct.
NEW QUESTION # 27
A CMDB Administrator wants to remove all Linux Servers in the organization that have not been updated in six months.
Which recommended action should the Administrator take in Data Foundations?
- A. Create a scheduled job
- B. Create an archive policy
- C. Create a business rule
Answer: B
Explanation:
Removing obsolete or inactive CIs from the CMDB must be handled carefully to avoid data loss, audit issues, and unintended operational impact. In ServiceNow, the recommended and governed approach is to use an archive policy.
Archive policies are designed to manage CI lifecycle cleanup based on defined conditions such as class, last updated date, lifecycle status, or operational state. In this scenario, the condition would target Linux Server CIs that have not been updated in six months. Archive policies can either archive or permanently delete records in a controlled, auditable manner, ensuring compliance with data retention and governance standards.
NEW QUESTION # 28
According to the Common Service Data Model (CSDM), a server team is requesting a catalog item be created for infrastructure requests.
Which role is involved in initiating the request and defining requirements?
- A. Enterprise Architect
- B. Application Service Owners
- C. Technology Service Owners
Answer: C
Explanation:
In CSDM, Technology Services (and their Service Offerings) represent how technical capabilities are delivered and consumed by internal teams. When a server team requests a catalog item for infrastructure services (e.g., VM provisioning, storage, OS builds), the role responsible for initiating the request and defining requirements is the Technology Service Owner.
Technology Service Owners understand the operational capabilities, constraints, SLAs, and fulfillment workflows required to deliver infrastructure services. They define catalog requirements such as options, approvals, fulfillment tasks, and guardrails--ensuring the request aligns with standardization, security, and operational readiness.
Application Service Owners focus on how applications are delivered and supported, not on defining infrastructure catalog items. Enterprise Architects provide standards and guidance but do not initiate or define catalog request requirements.
NEW QUESTION # 29
A Change Manager wants to gain value from CSDM.
How will the Change Management process benefit from CSDM? (Choose 2 options)
- A. Route the change dynamically
- B. Determine the root cause of the change issue
- C. Understand the impact of the change on services
- D. Identify blackout windows
Answer: C,D
Explanation:
CSDM significantly enhances Change Management by providing service-aware context, enabling better planning, risk assessment, and stakeholder communication.
One key benefit is the ability to identify blackout windows (Option A). Through CSDM-aligned Business Services, Service Offerings, and service calendars, Change Managers can clearly see when services are unavailable for change due to business constraints, regulatory requirements, or peak usage periods. This helps prevent changes from being scheduled during high-risk windows.
Another critical benefit is the ability to understand the impact of the change on services (Option D). CSDM establishes clear relationships between infrastructure CIs, Application Services, and Business Services. When a change is proposed, these relationships enable accurate impact analysis, allowing Change Managers to assess risk based on business criticality rather than just technical scope.
NEW QUESTION # 30
A customer's CMDB is aligned to the CSDM Walk stage.
What benefit is provided by the CMDB?
- A. Allows for additional stratification of technical teams' support structure along the lines of OLAs and commitments
- B. Improves the implementation velocity of APM Foundation for future business application rationalization
- C. Enables impact assessments for incident, problem, and change on Business Services
Answer: C
NEW QUESTION # 31
A development team is working on a project where an application will be deployed to many servers. There are several security requirements that must be checked to adhere to lawful regulatory compliance because the application will be holding customer personal data (PII and PCI).
Where in the CSDM should the development team store the information that will be used to satisfy audits?
- A. Customer Service Offerings and Databases
- B. Business Applications and Information Objects
- C. Technology Management Service Offerings (Technical Service Offerings) and Groups
Answer: B
Explanation:
Within the Common Service Data Model (CSDM), regulatory, security, and compliance-related information--especially for PII and PCI--must be modeled at the business and information level, not at the infrastructure or service offering level. The correct location for this data is Business Applications combined with Information Objects.
Business Applications represent the logical applications that support business capabilities and processes. Since compliance obligations (such as GDPR, PCI-DSS, or HIPAA) are assessed based on how the business uses data--not how many servers host the application--this is the correct anchor point for audit-relevant context.
Information Objects are explicitly designed to capture what data is processed, stored, or transmitted by an application, including data classifications such as PII, PCI, PHI, or confidential business data. They allow organizations to document regulatory scope, retention rules, encryption requirements, and audit controls without overloading CI records or polluting infrastructure classes.
NEW QUESTION # 32
A Platform Data Owner wants to improve data quality with reconciliation rules across five discovery sources.
The Data Owner knows the best option is to includeCMDB 360 / Multisource CMDBto manage and monitor discovery sources. The company currentlydoes not have the ITOM Discovery licenserequired for CMDB 360
/ Multisource CMDB.
What can the Data Owner do in this case?
- A. The IRE reconciliation rules can use discovery sources regardless of CMDB 360 being enabled
- B. CMDB 360 / Multisource is a platform product that can be used immediately
- C. ITOM Discovery must be purchased to take advantage of multisource IRE rules
Answer: A
Explanation:
TheIdentification and Reconciliation Engine (IRE)is acore platform capabilityinServiceNowand doesnot require CMDB 360 / Multisource CMDBto function. Even without the ITOM Discovery license, organizations can still define and useIRE reconciliation rulesacross multiple data sources.
IRE rules are source-aware and can evaluate attributes based onsource precedence, regardless of whether CMDB 360 is enabled. CMDB 360 enhances visibility, governance, and monitoring of multiple sources, but it isnot a prerequisitefor reconciliation logic itself.
Option A is incorrect because purchasing ITOM Discovery is not mandatory to use multisource reconciliation. Option C is also incorrect because CMDB 360 / Multisource CMDB is alicensed add-on, not a universally available platform feature.
Therefore, the Data Owner can proceed by configuringIRE reconciliation rules directly, makingOption Bthe correct answer.
NEW QUESTION # 33
(Choose 2 options)
A CMDB Administrator needs to create a new CI class for anInternet of Things (IoT) Sensorin ServiceNow.
What are therecommended practicesfor this activity?
- A. Add a new class under an appropriate parent class
- B. Modify an existing class
- C. Delete an unused class and replace it with the new one
- D. Install or update the CMDB CI Class Models Store application and verify the class does not already exist
Answer: A,D
Explanation:
Creating new CI classes is ahigh-impact configuration activityand must follow strictData Foundations and CSDM-aligned best practicesto avoid long-term technical debt and upgrade risk.
Option Bis a recommended first step. Before creating any new CI class, administrators shouldinstall or update the CMDB CI Class Models Store applicationand verify whether an appropriate class already exists.
ServiceNow frequently delivers new CI classes through updates and class model packages, and duplicating an existing or planned class can lead to fragmentation and governance issues.
Option Cis also correct. When a new class is truly required, it should beadded under an appropriate parent classto inherit attributes, behaviors, and discovery patterns. For an IoT Sensor, this might be under a hardware or device-related parent class, ensuring consistency and minimizing customization.
Option A is incorrect and dangerous-deleting unused classes can break dependencies and historical data.
Option D is also discouraged; modifying existing classes to repurpose them violates upgrade-safe design principles and can negatively impact discovery, integrations, and reporting.
By verifying existing models first and extending the class hierarchy correctly, organizations maintain aclean, scalable, and upgrade-safe CMDB.
Therefore, the correct answers areB and C.
NEW QUESTION # 34
An Asset Manager wants to ensure that Asset records and CI records are kept synchronized automatically.
How does the Manager do this? (Choose two.)
- A. Ensure that the business rule to update CI fields on change on the asset table is active
- B. Ensure one-to-one physical mapping between Asset and CI
- C. Ensure that scheduled jobs are run during off-business hours to ensure that sync happens
- D. Ensure that the business rule to update Asset fields on change on the CI table is active
Answer: A,D
Explanation:
In Data Foundations, "Govern" includes maintaining consistency between closely related data domains so that operational and asset lifecycle processes remain trustworthy. For hardware endpoints (and other asset-backed items), Asset and CI records often represent the same real- world item from two perspectives: financial/lifecycle management (Asset) and operational/service context (CI). Automatic synchronization prevents drift such as different owners, locations, or statuses appearing in Asset vs CI, which can cause reporting errors, incorrect fulfillment decisions, and audit issues.
The platform supports synchronization through out-of-box synchronization logic (commonly implemented as business rules and related configuration) that updates the CI when an Asset changes, and updates the Asset when a CI changes--so the records stay aligned regardless of which team updates which record. Therefore, ensuring the Asset-to-CI update logic is active (A) and the CI-to-Asset update logic is active (B) is the right way to keep data synchronized automatically.
NEW QUESTION # 35
Which type ofCMDB Data Manager policycreates tasks that allow the assigned individual toupdate fields on the CI record?
- A. Audit
- B. Certification
- C. Compliance
- D. Attestation
Answer: B
Explanation:
In CMDB governance, differentCMDB Data Manager policy typesserve different validation and enforcement purposes. When the objective is to allow an assigned individual toreview and update specific fields on a CI record, the correct policy type isCertification.
ACertification policycreates actionable tasks that require the assignee tovalidate and, if necessary, correct specific CI attributes, such as lifecycle status, support group, environment, or ownership. During certification, the user can directly update CI fields to bring the record into compliance with defined standards.
Attestation(Option C) only asks the user to confirm that a CIstill existsor is still valid; it does not require or enable attribute-level updates.Audit(Option A) is used for reporting and evidence collection, not remediation.
Compliance(Option D) measures adherence to rules but does not itself generate editable remediation tasks.
Certification is therefore the primary mechanism used whenhuman validation and correctionof CI data is required-making it a cornerstone of CMDB data quality management.
Hence, the correct answer isB - Certification.
NEW QUESTION # 36
Which type of CMDB Data Manager policy creates tasks that allow the assigned individual to update fields on the CI record?
- A. Audit
- B. Certification
- C. Compliance
- D. Attestation
Answer: B
Explanation:
In CMDB governance, different CMDB Data Manager policy types serve different validation and enforcement purposes. When the objective is to allow an assigned individual to review and update specific fields on a CI record, the correct policy type is Certification.
A Certification policy creates actionable tasks that require the assignee to validate and, if necessary, correct specific CI attributes, such as lifecycle status, support group, environment, or ownership. During certification, the user can directly update CI fields to bring the record into compliance with defined standards.
Attestation (Option C) only asks the user to confirm that a CI still exists or is still valid; it does not require or enable attribute-level updates. Audit (Option A) is used for reporting and evidence collection, not remediation. Compliance (Option D) measures adherence to rules but does not itself generate editable remediation tasks.
Certification is therefore the primary mechanism used when human validation and correction of CI data is required-making it a cornerstone of CMDB data quality management.
Hence, the correct answer is B - Certification.
NEW QUESTION # 37
Which default user groups are available when setting up a CMDB Data Manager policy and specifying the task assignment with the Assignment type set to "User Group Field"? (Choose 2 options)
- A. Assignment Group
- B. Managed By Group
- C. Support Group
- D. Owned by Group
Answer: A,B
Explanation:
In ServiceNow Data Foundations, specifically within CMDB Data Manager, policies are used to enforce data quality, completeness, and governance across configuration items (CIs). When defining a Data Manager policy, administrators can configure task creation for non-compliant records and specify how those tasks are assigned. One key configuration is the Assignment type, where "User Group Field" allows assignment to a group dynamically based on a group reference field on the CI record.
Out of the box, ServiceNow provides two default and universally available group reference fields for this purpose:
* Assignment Group
* Managed By Group
These two fields are considered core CMDB governance fields and are consistently available across most CI classes. They align directly with ITIL 4 Service Configuration Management and CSDM accountability models, ensuring that remediation tasks are routed to teams responsible for operational ownership or technical management of the CI.
Assignment Group
This is the most commonly used operational field in ServiceNow. It represents the team responsible for working on tasks related to the CI and is fully supported by CMDB Data Manager for automated task assignment.
Managed By Group
This field represents the group accountable for managing the CI throughout its lifecycle. It is a standard CMDB field and is explicitly supported by Data Manager policies for governance-driven task routing.
NEW QUESTION # 38
User endpoint devices are imported into the CMDB and populate the Assigned to [assigned_to] field on the Computer [cmdb_ci_computer] CI. The Asset team requests that Configuration Analysts populate the Assigned to field on the related Asset.
What action does a Configuration Analyst take to achieve this in an automated way?
- A. Use the Asset CI Field Mapping module to create a new rule to replicate the "Assigned to" value between the asset and associated CI
- B. Configure a business rule on the computer table to use a script to populate the "Assigned to" field on the asset based on insert or update in the computer class "Assigned to" field
- C. Hide the "Assigned to" field on the asset record and create a new field that dot-walks to the related CI to get the "Assigned to" value
Answer: A
Explanation:
Data Foundations strongly encourages using out-of-box synchronization mechanisms rather than custom scripting whenever possible, to reduce technical debt and improve upgrade safety. In this scenario, endpoint data is being ingested into the CI record, and the Asset team needs the corresponding Asset record kept in sync automatically for their asset management processes.
The recommended approach is to use Asset CI Field Mapping, which is designed specifically to map and synchronize fields between an Asset and its related CI. Creating or updating a mapping rule for "Assigned to" allows the platform to replicate the value in a controlled, supportable way without writing scripts. This approach aligns with best practices: standard configuration, clear governance, and minimal custom code.
NEW QUESTION # 39
A Configuration Manager wants to use theUnified Map.
Where would it be accessed?
- A. CMDB Workspace
- B. CMDB Data Manager
- C. CI Class Manager
Answer: A
Explanation:
TheUnified Mapis a visualization capability used to understandservice composition, dependencies, and relationshipsacross CIs, Application Services, and infrastructure. InServiceNow, the Unified Map is accessed through theCMDB Workspace.
CMDB Workspace serves as the central experience for CMDB operations, analytics, and visualization. From within the workspace, users can launch the Unified Map to explore how services are constructed, identify dependencies, and analyze impact-leveraging data from Discovery and Service Mapping.
Option A (CI Class Manager) is used forclass hierarchy, ownership, and principal class configuration, not visualization. Option B (CMDB Data Manager) is focused ongovernance and lifecycle policies, such as archival, certification, and attestation, not service mapping views.
Because Unified Map is anoperational and analytical visualization tool, it is correctly accessed viaCMDB Workspace.
Therefore, the correct answer isC - CMDB Workspace.
NEW QUESTION # 40
A Configuration Manager has configured multiple data sources that are all authorized to update thesame class and the same set of class attributesin the CMDB.
What can the Configuration Manager do to controlwhich data source should be the authoritative source of truthfor a specific class or set of class attributes?
- A. Manually run the data source updates in the correct order
- B. Assign a priority to each data source in reconciliation rules
- C. Configure data refresh rules with a specific time period
- D. Assign a run order to each data source in the identification rules
Answer: B
Explanation:
InServiceNow, controllingsource precedencewhen multiple authorized data sources update the same CI attributes is a core responsibility ofIdentification and Reconciliation Engine (IRE)governance.
The correct and supported method is toassign priority to each data source in reconciliation rules.
Reconciliation rules determinewhich source winswhen multiple sources attempt to update the same attribute on a CI. By defining source precedence, the Configuration Manager ensures that themost authoritative system of record(for example, Discovery over manual imports, or HR systems over spreadsheets) consistently controls specific attributes or classes.
Option B is incorrect because manually sequencing data source runs is unreliable, does not scale, and violates Data Foundations best practices. Option C only controls how often data is refreshed, not which source is authoritative. Option D is incorrect becauseidentification rulesare used to uniquely identify CIs-not to control attribute-level precedence.
Using reconciliation rules providesdeterministic, auditable, and automated control, which is essential for maintaining CMDB trust and avoiding data conflicts.
Therefore, the correct answer isA - Assign a priority to each data source in reconciliation rules.
NEW QUESTION # 41
The Apache Web Server Identification Rule is configured with the following criterion attributes:
Class
Configuration file
Version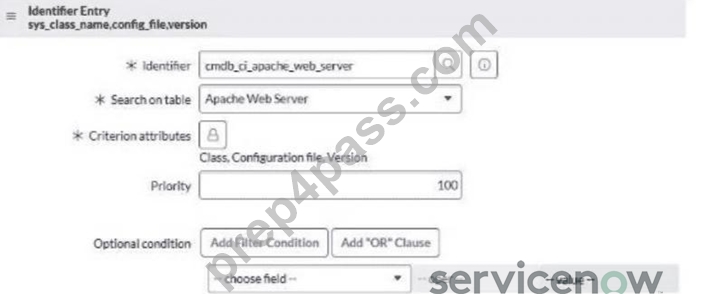
Yesterday, an Apache Web Server CI was discovered as part of Service Mapping.
Today, the application owner upgraded Apache to a different version and reran discovery of the service.
What will happen in the CMDB?
- A. The Apache Web Server CI will be reclassified as a Web Server CI.
- B. A duplication error will occur.
- C. A new Apache Web Server CI is created.
- D. The existing Apache Web Server CI will be reconciled and its version will be updated.
Answer: C
Explanation:
This scenario hinges on how the Identification and Reconciliation Engine (IRE) in ServiceNow evaluates identification rules.
The identification rule for the Apache Web Server class includes Version as part of the identifier criteria, along with Class and Configuration file. Identification rules must match all criterion attributes exactly for an incoming record to be identified as an existing CI and reconciled.
Yesterday's discovery created an Apache Web Server CI with a specific version value. When Apache is upgraded and discovery is rerun, the Version attribute changes. Because Version is part of the identifier, the incoming record no longer matches the existing CI's identifier entry. As a result, the IRE cannot identify the existing CI as the same configuration item.
When identification fails and no matching identifier entry is found, the IRE proceeds to insert a new CI record rather than updating the existing one. This behavior is intentional and protects the CMDB from incorrectly reconciling records that no longer meet identification criteria.
Option A is incorrect because reconciliation only occurs after successful identification.
Option C is incorrect because reclassification is unrelated to identification criteria.
Option D is incorrect because this is not an error condition; it is expected IRE behavior.
This example highlights a best practice caution: volatile attributes (such as Version) should generally not be used as identifier attributes, as they can cause unintended CI duplication during upgrades.
NEW QUESTION # 42
An organization wants visibility of which business applications are supported by a specific database server. What modeling enables this?
- A. Asset relationships
- B. Task relationships
- C. Application Service dependency mapping
- D. Server to Business Service direct relationship
Answer: C
Explanation:
Servers should link to Application Services, which then relate to Business Applications or Business Services.
NEW QUESTION # 43
What is the relationship between an Application and a Server?
- A. Application > Uses::Used by > Server
- B. Application > Used by::Uses > Server
- C. Application > Runs on::Runs > Server
- D. Application > Runs::Runs On > Server
Answer: C
Explanation:
In Data Foundations (CMDB and CSDM), relationship modeling must reflect real operational dependency so that incident triage, change impact analysis, and service visibility remain accurate. When an Application is hosted on a Server, the standard hosting-style relationship used in CMDB relationship governance is expressed as "Runs on::Runs". This pairing represents the two directional descriptors of the same relationship type: from the application perspective it runs on the server, and from the server perspective it runs the application.
This matters because CMDB relationships are used by downstream capabilities (for example, dependency views, impact calculations, and governance rules). Using the correct out-of-box relationship descriptor pair ensures consistent reporting and prevents confusion when teams traverse relationships "upstream" and "downstream." In addition, relationship governance rules and inheritance are commonly built around standard relationship types; using the correct "Runs on::Runs" semantics supports validation across subclasses (for example, specific application and server subclasses) without requiring custom relationship definitions.
NEW QUESTION # 44
A Configuration Management Process Owner is preparing solution options for presentation to technical governance for ingesting custom CIs into the CMDB. The solution must align with best practices, minimize future technical debt, and ensure upgrade compliance.
Which solutions accomplish this? (Choose 2 options)
- A. Repurposing a base CI class and renaming attributes as required
- B. Extending an existing CI class table to accommodate the custom CI class attributes
- C. Installing or upgrading the CMDB CI Class Models Store application to find a suitable existing CI class accommodating any new attributes
- D. Extending the existing Asset class table to custom CI class attributes
Answer: B,C
Explanation:
In ServiceNow, ingesting custom CIs must be done with a strong focus on upgrade safety, governance, and long-term maintainability. Data Foundations guidance explicitly discourages repurposing or overloading base classes, as this creates technical debt and upgrade risk.
Option B is a best practice because the CMDB CI Class Models Store delivers ServiceNow- supported CI classes that align with platform evolution. Before creating or extending classes, administrators should verify whether a suitable class already exists or has been introduced in newer releases. This avoids duplication and ensures future compatibility.
Option D is also correct. When no suitable class exists, extending an existing CI class (under the appropriate parent) to add required attributes preserves inheritance, discovery behavior, reporting, and upgrade compatibility. This approach is preferred over creating entirely new, disconnected schemas.
NEW QUESTION # 45
......
ServiceNow CIS-DF Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
| Topic 5 |
|
Real Updated CIS-DF Questions & Answers Pass Your Exam Easily: https://www.prep4pass.com/CIS-DF_exam-braindumps.html
Easily To Pass New CIS-DF Verified & Correct Answers: https://drive.google.com/open?id=19YWEfIUXFW3xVOSO3cWD11HPsysNwMyL
