

[2022] Essentials by Fireware Essentials Actual Free Exam Practice Test
Free Fireware Essentials Essentials Exam Question
Who should take the Essentials Exam
The Essential Exam certification is an internationally-recognized certification which help to have validation for those professionals who are keen to make their career in configuring and managing Firebox devices that run Fireware.
if a candidate/professional seeks a powerful improvement in career growth needs enhanced knowledge, skills, and talents. The Essential certification provides proof of this advanced knowledge and skill.
The benefit of obtaining the Essential Exam Certification
- Essential exam certification credential will give you edge over other counterparts. Apart from knowledge from Essential Exam.
- Essential exam certification will help you in providing strong understanding about Fireware Essentials, along with basic networking and new Fireware topics.
- It help you to make your career into WatchGaurd network security, Essential exam will help you to get respectful plus highly paid jobs into Market.
- Essential exam Certification will provide you digital badge which you can add it to your CV, profile, linkedin etc. which would be bringing more recruiting Companies towards your profile.
- Most of the hiring manager prefer to hire candidates who are already certified and having expertise into that domain. Company use to perform calculation because they use to spend lots of money on conducting training for the candidates who have zero knowledge about WatchGaurd Security. They use to prefer candidates who are already certified because definitely they would be having enough knowledge to start contributing to the production.
NEW QUESTION 35
Match each WatchGuard Subscription Service with its function.
Controls access to website based on content categories. . (Choose one).
- A. Application Control
- B. Gateway / Antivirus
- C. Intrusion Prevention Server IPS
- D. Reputation Enable Defense RED
- E. Explanation:
WebBlocker controls access to the good and bad places that are reachable on the web,preventing users from gaining access to sites that have evil intentions.
If you configure WebBlocker to use the Websense cloud for WebBlocker lookups, WebBlocker uses the Websense content categories. A web site is added to a category when the content of the web site meets the criteria for the content category.
Reference:http://www.tomsitpro.com/articles/network-security-solutions-guide, 2-866-6.html
QUESTIONNO: 74
Match each type of NAT with the correct description:
Allows a user on the trusted or optional network to connect to a public server that is on the same physical Firebox interface by its public IP address or domain name. (Choose one)
A. 1-to1 NAT
B. Dynamic NAT
C. NAT Loopback - F. WebBlocker
Answer: F
Explanation:
NAT loopback allows a user on the trusted or optional networks to get access to a public server that is on the same physical Firebox or XTM device interface by its public IP address or domain name.
Reference:http://www.watchguard.com/help/docs/wsm/11/en-US/index_Left.html#CSHID=en-US%2Fnat%2Fnat_loopback_c.html|StartTopic=Content%2FenUS%2Fnat%2Fnat_loopback_c.html
NEW QUESTION 36
Which WatchGuard tools can you use to review the log messages generated by your Firebox? (Select three).
- A. Fireware XTM Web UI > Traffic Monitor
- B. Dimension > Log manager
- C. Firebox SystemManager > Traffic Monitor
- D. WatchGuard System Manager > Policy Manager
- E. Firebox System Manager > Status Report
Answer: A,B,C
Explanation:
A: You can use Firebox System Manager (FSM) to see log messages from your XTM device as they occur.
Reference:http://www.watchguard.com/help/docs/wsm/xtm_11/en-US/index.html#cshid=en-US/fsm/log_msgs_traffic_mon_wsm.html
D: You can use Firebox System Manager to see log messages in real-time on the Traffic Monitor tab. You can also examine log messages with Log Manager or WatchGuard Dimension.
B: After you connect to WatchGuard WebCenter, you can review the log messages sent from your XTM devices to your WatchGuard Log Server. Log Manager enables you to see log messages from your device for any period of time you specify, if log messages were generated in the selected time frame. To see log messages for an XTM device as they are generated, in real-time, you can use Firebox System Manager Traffic Monitor.
Reference:http://www.watchguard.com/help/docs/wsm/XTM_11/en-US/index.html#en-US/logging/log_mgr_view_device_wsm.html
Incorrect:
Not C: The Status Report tab shows statistics about Firebox orXTM device traffic and performance. It does not display log messages.
To see the Status Report:
Start Firebox System Manager.
Select the Status Report tab.
Screen shot of the Firebox System Manager Status Report
NEW QUESTION 37
You configured four Device Administrator user accounts for your Firebox. To see a report of witch Device Management users have made changes to the device configuration, what must you do? (Select two.)
- A. Configure your device to send audit trail log messages to your WatchGuard Log Server or Dimension Log Server.
- B. Open WatchGuard Server Center and review the configuration history for managed devices.
- C. Start Firebox System Manager for the device and review the activity for the Management Users on the Authentication List tab.
- D. Connect to Report Manager or Dimension and view the Audit Trail report for your device.
Answer: B,D
NEW QUESTION 38
After you enable spamBlocker, your users experience no reduction in the amount of spam they receive. What could explain this? (Select three.)
- A. The Maximum File Size to Scan option is set too high.
- B. A spamBlocker exception is configured to allow traffic from sender *.
- C. spamBlocker Virus Outbreak Detection is not enabled.
- D. Connections cannot be resolved to the spamBlocker servers because DNS is not configured on the Firebox.
- E. The spamBlocker action for Confirmed Spam is set to Allow.
Answer: B,D,E
Explanation:
Explanation/Reference:
A: Spamblocker requires DNS to be configured on your XTM device
B: If you use spamBlocker with the POP3 proxy, you have only two actions to choose from: Add Subject Tag and Allow. Allow lets spam email messages go through the Firebox without a tag.
D: The Firebox might sometimes identify a message as spam when it is not spam. If you know the address of the sender, you can configure the Firebox with an exception that tells it not to examine messages from that source address or domain.
Reference: Fireware Basics, Courseware: WatchGuard System Manager 10, page 138
NEW QUESTION 39
After you enable Gateway AntiVirus, IPS, or Application control, how can you make sure the services protect your network from the latest known threats? (Select one.)
- A. Configure reputation Enabled Defense.
- B. Enable default packet handling.
- C. Enable automatic signature updates.
- D. Enable HTTPS deep inspection.
Answer: C
NEW QUESTION 40
You need to create an HTTP-proxy policy to a specific domain for software updates (example.com). The update site has multiple subdomains and dynamic IP addresses on a content delivery network. Which of these options is the best way to define the destination in your HTTP-proxy policy? (Select one.)
- A. Add IP addresses that correspond to each software update server in the domain.
- B. Create an alias for all subdomains and known IP addresses for example.com.
- C. Configure an FQDN for *.example.com.
- D. Configure a host name for update.example.com.
Answer: A
NEW QUESTION 41
HOTSPOT
Match the monitoring tool to the correct task: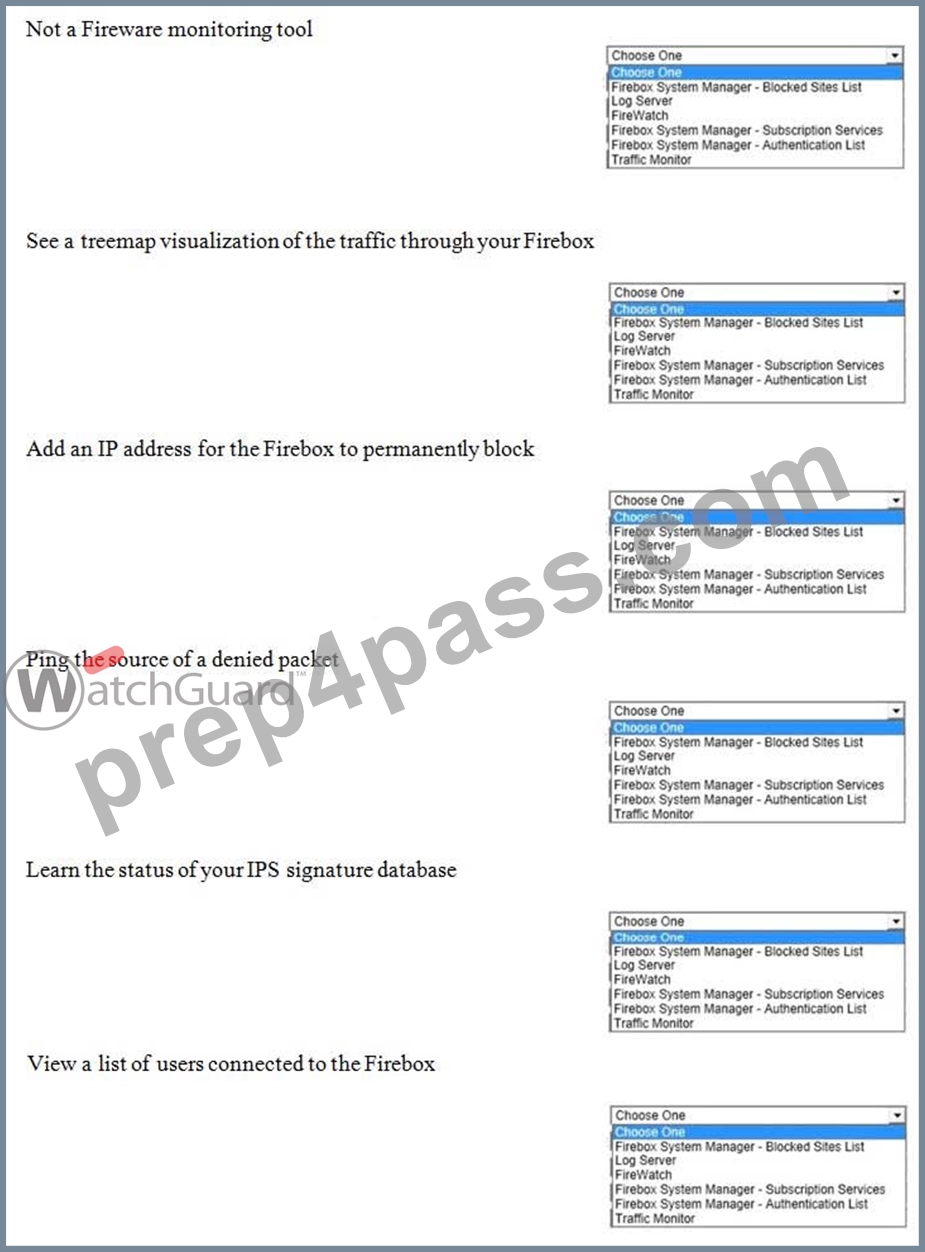
Answer:
Explanation: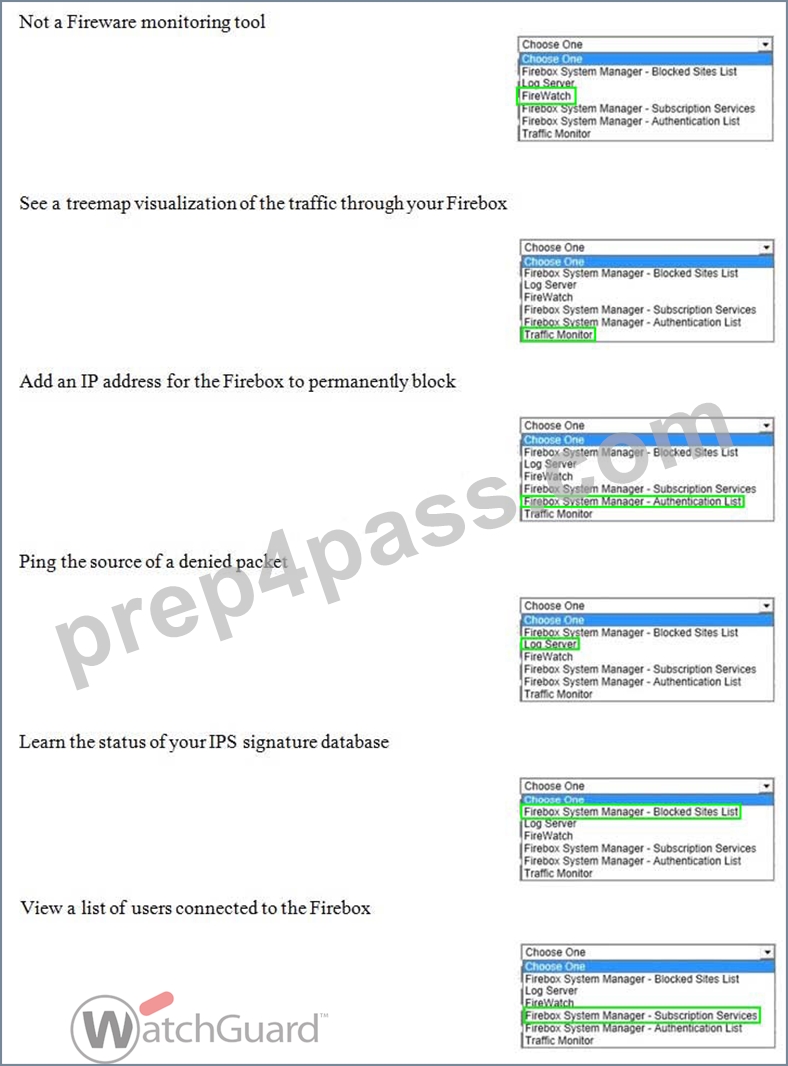
Explanation:
Firewatch Traffic Monitor Firebox system Manager - Authentication List Log Server Firbox System Manager - Blocked State List Firebox System Manager - Subscription Services
NEW QUESTION 42
Which tool can add an IP address for the Firebox to permanently block? (Select one)
- A. Traffic Monitor
- B. Log Server
- C. Firebox System Manager - Subscription services
- D. FireBox System Manager - Blocked Sites list
- E. Firebox System Manager - Authentication list
- F. FireWatch
Answer: D
Explanation:
Block a site permanently
The Successful Company networkadministrator has been driven to distraction recently by a script kiddy using addresses in the 192.136.15.0/24 network to run probes of the Successful network. In this exercise, we permanently block all connections from that network.
1.From PolicyManager, select Setup > Default Threat Protection > Blocked Sites. The Blocked Sites Configuration dialog box opens.
2.On the Blocked Sites tab, click Add.
3.The Add Site dialog box opens. 3. Use the Choose Type drop-down list to select Network IP. In the Value text box, type 192.136.15.0/ 24.
4. Click OK.
The entry appears in the Blocked Sites list. With this configuration, the Firebox blocks all packets to and from the 192.136.15.0/24 network range.
Reference: Fireware Basics, Courseware: WatchGuard System Manager 10, pages 15, 34, 59, 181
NEW QUESTION 43
With the policies configured as shown in this image, HTTP traffic can be sent and received through branch office VPN tunnel.1 and tunnel.2.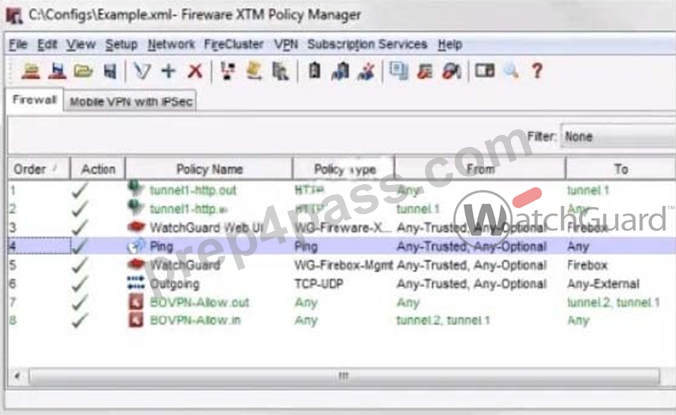
- A. True
- B. False
Answer: A
NEW QUESTION 44
When your users connect to the Authentication Portal page to authenticate, they see a security warning message in their browses, which they must accept before they can authenticate. How can you make sure they do not see this security warning message in their browsers? (Select one.)
- A. Replace the Firebox certificate with the trusted certificate from your web server.
- B. Instruct them to disable security warning message in their preferred browsers.
- C. Import a custom self-signed certificate or a third-party certificate to your Firebox and import the same certificate to all client computers or web browsers.
- D. Add the user accounts for your users who use the Authentication Portal to a list of trusted users on your Firebox.
Answer: C
NEW QUESTION 45
Which policies can use the Intrusion Prevention Service to block network attacks? (Select one?)
- A. Only packet filter policies
- B. Only HTTP and HTTPS Proxy policies
- C. All policies
- D. Only proxy policies
- E. Only inbound policies
Answer: A
NEW QUESTION 46
An email newsletter about sales from an external company is sometimes blocked by spamBlocker. What option could you choose to make sure the newsletter is delivered to your users? (Select one.)
- A. Add a spamBlocker exception based on the From field of the newsletter email.
- B. Set the spamBlocker action to quarantine the email for later retrieval.
- C. Set the spamBlocker virus outbreak detection action to allow emails from the newsletter source.
- D. Add a spamBlocker subject tag for bulk email messages.
Answer: D
NEW QUESTION 47
In this diagram, which branch office VPN tunnel route must you add on the Site A Firebox to allow traffic between devices on the trusted network at Site A and the trusted network at site B? (Select one.)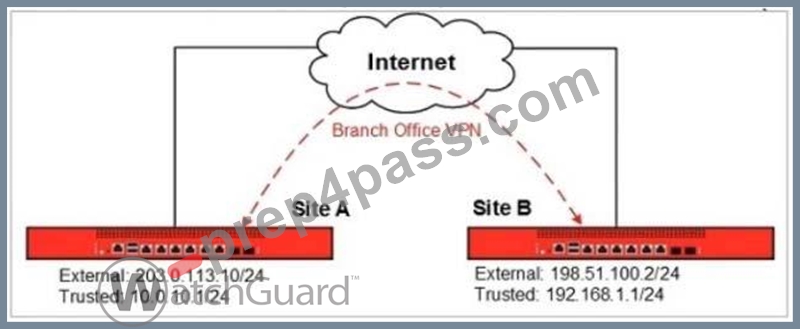
- A. Local: 10.0.10.0/24 <--> Remote: 192.168.1.0/24
- B. Local: 192.168.1.0/24 <--> Remote: 10.0.10.0/24
- C. Local: 203.0.113.10/24 <--> Remote: 198.151.100.2/24
- D. Local: 10.0.10.1/24 <--> Remote: 192.168.1.1/24
Answer: D
Explanation:
Explanation/Reference:
The local, Site A, network is 10.0.10.1/24 while the remote, Site B, network is 192.168.1.1/24.
NEW QUESTION 48
What settings must you device configuration file include for Gateway AntiVirus to protect users on your network? (Select two.)
- A. Install the Gateway AntiVirus server on your network.
- B. Disable automatic signature updates.
- C. Configure Gateway AntiVirus settings for a proxy action.
- D. Configure a policy to use a proxy action that has AntiVirus settings configured.
- E. Decrease the scan limits
Answer: C,D
Explanation:
Explanation/Reference:
When you enable Gateway AntiVirus, you must set the actions to be taken if a virus or error is found in an email message (SMTP or POP3 proxies), web page download or upload post (HTTP proxy), or uploaded or downloaded file (FTP proxy). When Gateway AntiVirus is enabled, it scans each file up to a specified kilobyte count. Any additional bytes in the file are not scanned. This allows the proxy to partially scan very large files without a large effect on performance.
Reference: http://watchguard.com/help/docs/webui/xtm_11/en-us/content/en-us/services/gateway_av/ av_actions_config_c.html
NEW QUESTION 49
You can configure your Firebox to automatically redirect users to the Authentication Portal page.
- A. True
- B. False
Answer: A
NEW QUESTION 50
Match the monitoring tool to the correct task.
Which is not a Fireware monitoring tool? (Select one)
- A. Log Server
- B. Traffic Monitor
- C. Firebox System Manager - Subscription services
- D. Firebox System Manager - Authentication list
- E. FireWatch
- F. FireBox System Manager - Blocked Sites list
Answer: A
Explanation:
Explanation/Reference:
The Fireware monitor and configuration tools are: Edge Web Manager, Firebox System Manager, HostWatch, and Ping.
Reference: Fireware Basics, Courseware: WatchGuard System Manager 10, pages 15, 34, 59, 181
NEW QUESTION 51
......
WatchGuard Essentials Actual Questions and Braindumps: https://www.prep4pass.com/Essentials_exam-braindumps.html
Essentials dumps & Fireware Essentials sure practice dumps: https://drive.google.com/open?id=1wmDtKrUBslJ5d4msFE4HBprydXyPyQgu
