

Essentials Dumps (2023) Prepare Your Exam With 75 Questions
New Essentials Dumps - Real WatchGuard Exam Questions
NEW QUESTION 25
HOTSPOT
Match each type of NAT with the correct description: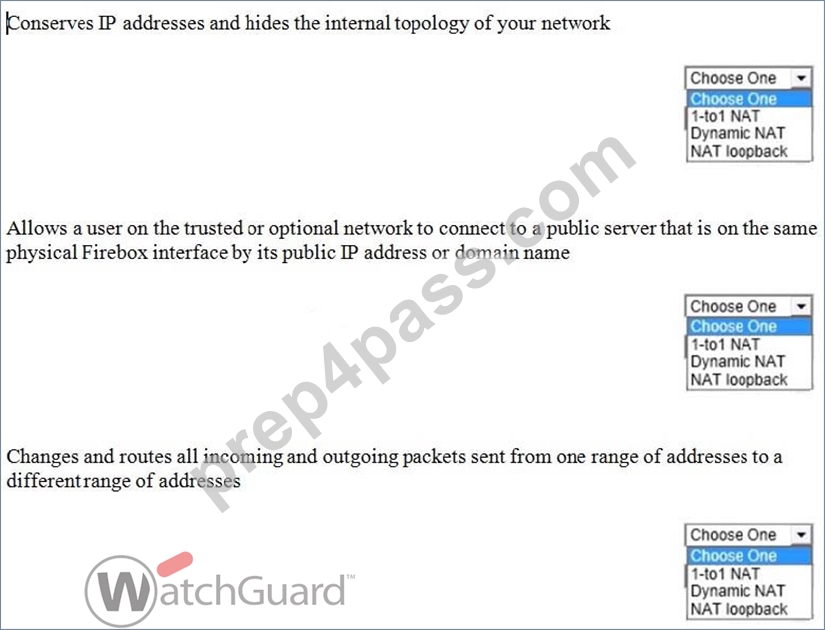
Answer:
Explanation: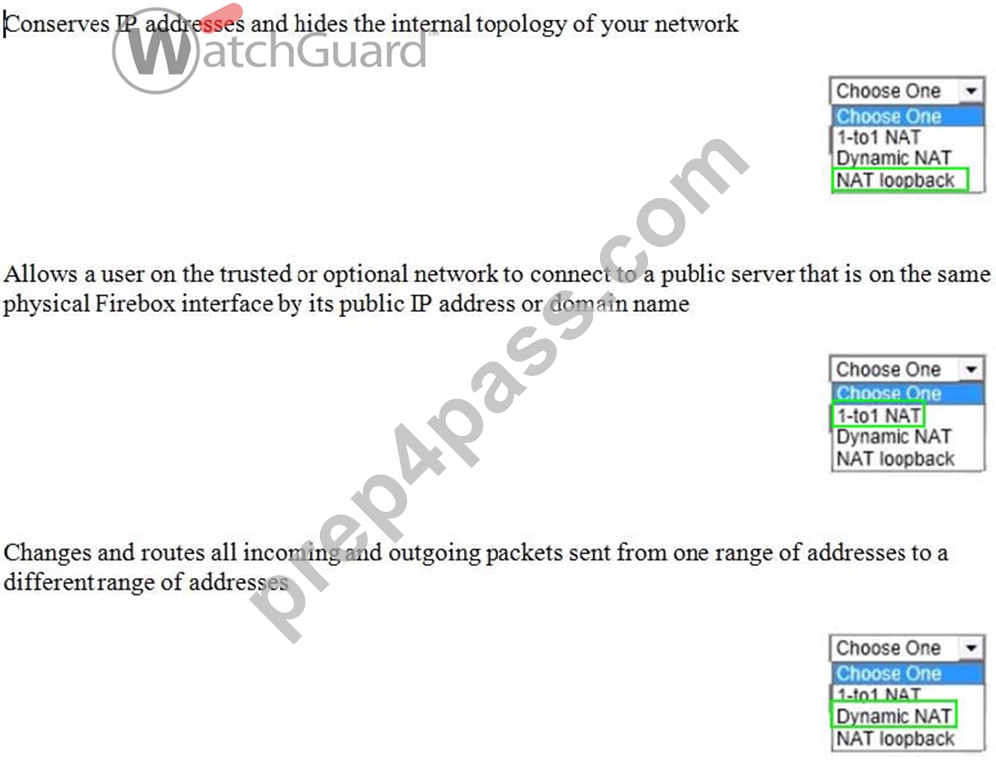
Explanation:
NAT Loopback 1-to 1 NAT
Dynamic NAT
NEW QUESTION 26
How is a proxy policy different from a packet filter policy? (Select two.)
- A. Only a proxy policy uses the IP source, destination, and port to control network traffic.
- B. Only a proxy policy can prevent specific threats without blocking the entire connection.
- C. Only a proxy policy examines information in the IP header.
- D. Only a proxy works ta the application, network, and transport layers to examine all connection data.
Answer: A,D
NEW QUESTION 27
You need to create an HTTP-proxy policy to a specific domain for software updates (example.com). The update site has multiple subdomains and dynamic IP addresses on a content delivery network. Which of these options is the best way to define the destination in your HTTP-proxy policy? (Select one.)
- A. Add IP addresses that correspond to each software update server in the domain.
- B. Configure a host name for update.example.com.
- C. Create an alias for all subdomains and known IP addresses for example.com.
- D. Configure an FQDN for *.example.com.
Answer: A
NEW QUESTION 28
For which of these third party authentication methods must you specify a search base? (Select two.)
- A. RADIUS
- B. SecurID
- C. LDAP
- D. Active Directory
Answer: C,D
Explanation:
Explanation/Reference:
B: Configuring the Firebox to use Active Directory authentication is similar to the process for LDAP authentication. You must set a search base to put limits on the directories on the authentication server the Firebox searches in for an authentication match.
D: When you configure the Firebox to use LDAP authentication, you must set a search base to put limits on the directories on the authentication server the Firebox searches in for an authentication match Reference: Fireware Basics, Courseware: WatchGuard System Manager 10, page 83-84
NEW QUESTION 29
From the Fireware Web UI, you can generate a report that shows your device configuration settings.
- A. True
- B. False
Answer: A
NEW QUESTION 30
In this diagram, which branch office VPN tunnel route must you add on the Site A Firebox to allow traffic between devices on the trusted network at Site A and the trusted network at site B? (Select one.)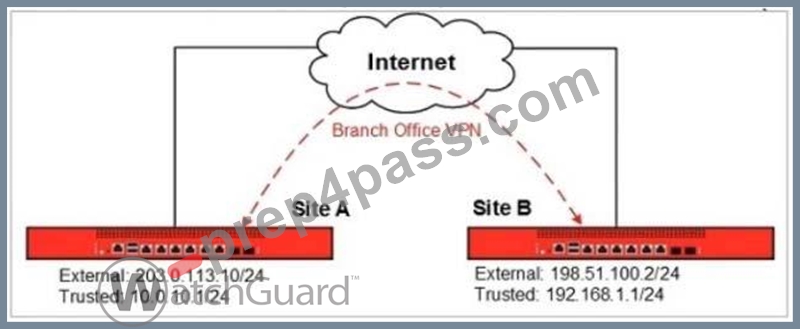
- A. Local: 203.0.113.10/24 <--> Remote: 198.151.100.2/24
- B. Local: 10.0.10.1/24 <--> Remote: 192.168.1.1/24
- C. Local: 10.0.10.0/24 <--> Remote: 192.168.1.0/24
- D. Local: 192.168.1.0/24 <--> Remote: 10.0.10.0/24
Answer: B
Explanation:
Explanation/Reference:
The local, Site A, network is 10.0.10.1/24 while the remote, Site B, network is 192.168.1.1/24.
NEW QUESTION 31
In a Mobile VPN configuration, why would you choose default route VPN over split tunnel VPN? (Select one.)
- A. Default route VPN uses less processing power
- B. Default route VPN uses less bandwidth
- C. Default route VPN allows your Firebox to examine all remote user traffic
- D. Default route VPN automatically allows dynamic NAT
Answer: C
NEW QUESTION 32
Which WatchGuard Subscription Service must be enabled in a proxy policy before you can use APT Blocker? (Select one.)
- A. IPS
- B. Gateway Antivirus
- C. RED
- D. Application Control
- E. WebBlocker
Answer: B
NEW QUESTION 33
How is a proxy policy different from a packet filter policy? (Select two.)
- A. Only a proxy works at the application, network, and transport layers to examine all connection data.
- B. Only a proxy policy examines information in the IP header.
- C. Only a proxy policy uses the IP source, destination, and port to control network traffic.
- D. Only a proxy policy can prevent specific threats without blocking the entire connection.
Answer: A,D
Explanation:
Explanation/Reference:
C: Proxies can prevent potential threats from reaching your network without blocking the entire connection.
D: A proxy operates at the application layer, as well as the network and transport layers of a TCP/IP packet, while a packet filter operates only at the network and transport protocol layers.
Incorrect:
Not A: A packet filter examines each packet's IP header to control the network traffic into and out of your network.
Reference: Fireware Basics, Courseware: WatchGuard System Manager 10, page 95
NEW QUESTION 34
In the network configuration in this image, which aliases is Eth2 a member of? (Select three.)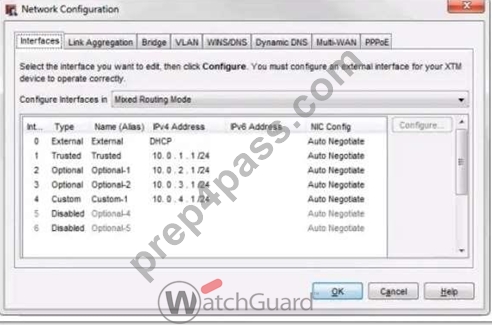
- A. Optional-1
- B. Any-External
- C. Any
- D. Any-optional
- E. Any-Trusted
Answer: A,C,D
NEW QUESTION 35
Your company denies downloads of executable files from all websites. What can you do to allow users on the network to download executable files from the company's remote website? (Select one.)
- A. Configure HTTP Request > URL Paths to allow the company's remote website.
- B. Create a WebBlocker exception to allow access to the company's remote website.
- C. Add an HTTP proxy exception for the company's remote website.
- D. Create a Blocked Sites exception.
- E. Create an IPS exception.
Answer: C
NEW QUESTION 36
You can configure your Firebox to send log messages to how many WatchGuard Log Servers at the same time? (Select one.)
- A. As many as you have configured on your network.
- B. Two
- C. One
Answer: A
NEW QUESTION 37
Which policies can use the Intrusion Prevention Service to block network attacks? (Select one?)
- A. Only proxy policies
- B. All policies
- C. Only inbound policies
- D. Only HTTP and HTTPS Proxy policies
- E. Only packet filter policies
Answer: E
NEW QUESTION 38
The policies in a default Firebox configuration do not allow outgoing traffic from optional interfaces.
- A. False
- B. True
Answer: A
NEW QUESTION 39
To prevent certificate error warnings in your browser when you use deep content inspection with the HTTPS proxy, you can export the proxy authority certificate from the Firebox and import that certificate to all client devices.
- A. True
- B. False
Answer: A
NEW QUESTION 40
Match each WatchGuard Subscription Service with its function.
Uses full-system emulation analysis to identify characteristics and behavior of zero-day malware. (Choose one).
- A. Spam Blocker
- B. Intrusion Prevention Server IPS
- C. APT Blocker
- D. Gateway / Antivirus
- E. DataLoss Prevention DLP
- F. Reputation Enable Defense RED
- G. Application Control
- H. Quarantine Server
- I. WebBlocker
Answer: C
Explanation:
APT Blocker is intended to stop malware and zero-day threats that are trying to invade anorganization's network.
APT Blocker uses a next-gen sandbox to get detailed views into the execution of a malware program. After first running through other security services, files are fingerprinted and checked against an existing database - first on theappliance and then in the cloud. If the file has never been seen before, it is analyzed using the system emulator, which monitors the execution of all instructions. It can spot the evasion techniques that other sandboxes miss.
Reference:http://www.watchguard.com/wgrd-products/security-modules/apt-blocker
NEW QUESTION 41
......
Get Ready with Essentials Exam Dumps: https://www.prep4pass.com/Essentials_exam-braindumps.html
Dependable Essentials Exam Dumps to Become WatchGuard Certified: https://drive.google.com/open?id=1wmDtKrUBslJ5d4msFE4HBprydXyPyQgu
